Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.
This feature is developed by yu-i-i/overleaf-cep. Here we offers some documents for your configuration.
Configuration
Internally, Overleaf OIDC module uses the passport-openidconnect library. If you are having issues configuring OpenID Connect, it is worth reading the README for passport-openidconnect to get a feel for the configuration it expects.The environment variable EXTERNAL_AUTH is required to enable the OIDC authentication module. This environment variable specifies which external authentication methods are activated. The value of this variable is a list. If the list includes oidc then OIDC authentication will be activated.For example: EXTERNAL_AUTH=ldap oidcWhen using the OIDC authentication method, a user is redirected to the Identity Provider (IdP) authentication site. If the IdP successfully authenticates the user, the Overleaf users database is checked for a record containing a thirdPartyIdentifiers field structured as follows:
The externalUserId must match the user ID in the profile returned by the IdP server (see the OVERLEAF_OIDC_USER_ID_FIELD environment variable), and providerId must match the ID of the OIDC provider (see the OVERLEAF_OIDC_PROVIDER_ID).If no matching record is found, the database is searched for a user with the primary email address matching the email in the IdP user profile:
If such a user is found, the thirdPartyIdentifiers field is updated.
If no matching user is found and JIT account creation is not disabled, a new user is created with the email address and thirdPartyIdentifiers from the IdP profile.
In both cases, the user is said to be ‘linked’ to the external OIDC user. The user can be unlinked from the OIDC provider on the /user/settings page.
Finding the values with the discovery document
Every OpenID Provider (OP) publishes a discovery document at <issuer>/.well-known/openid-configuration. Copy the values from it instead of typing them by hand; one wrong character is enough to break the login.
1
Find the discovery URL
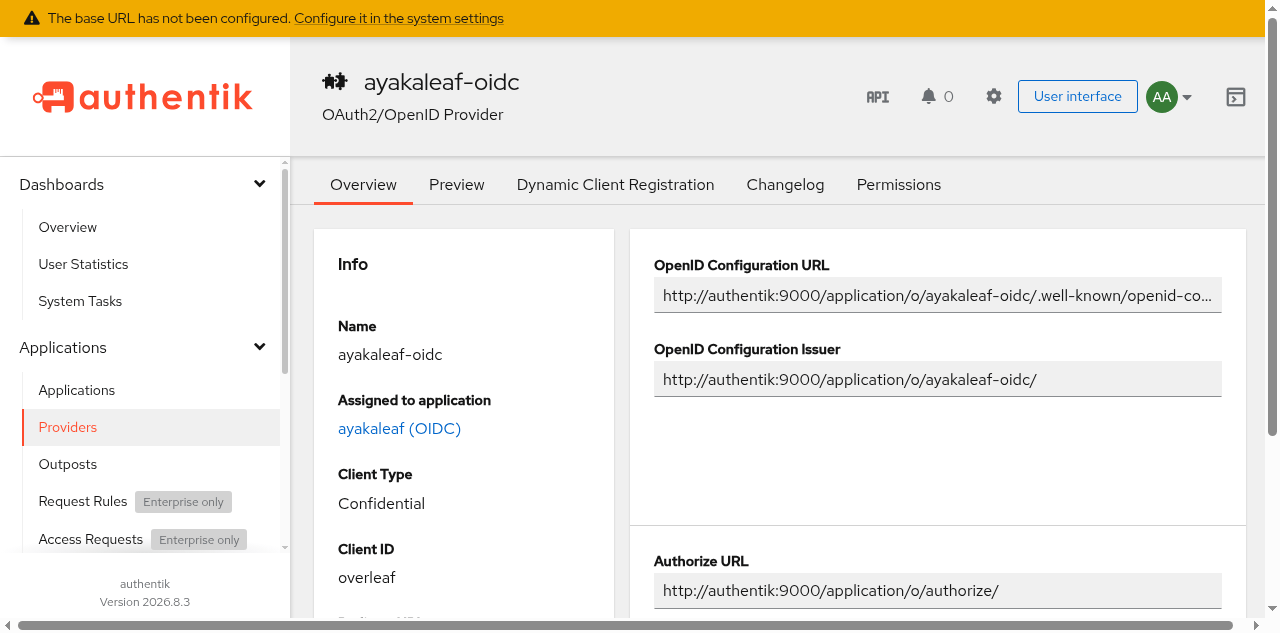
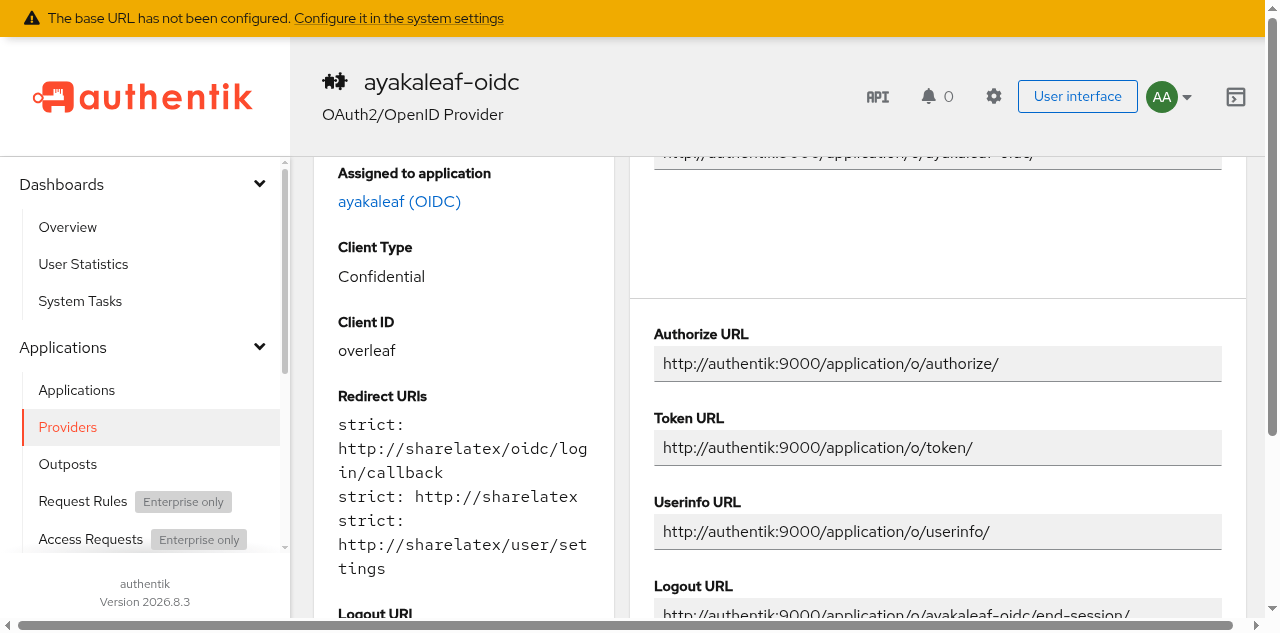
Your OP shows it on the page of the client (provider) you created for Overleaf. In Authentik, open Applications > Providers, select the provider and look for OpenID Configuration URL and OpenID Configuration Issuer:
Authentik: the discovery URL and the issuer of a provider (test instance)
Copy issuer exactly, including the trailing slash. Overleaf compares it character by character with the issuer in the ID token; any difference makes every OIDC login fail with:{"message":{"message":"ID token not issued by expected OpenID provider."}}In Authentik the issuer belongs to the application (.../application/o/<application-slug>/). It is not the address of the Authentik server, although the authorize, token and userinfo URLs are shared by all applications.
Environment Variables
The values of the following five required variables can be found using .well-known/openid-configuration endpoint of your OpenID Provider (OP), see above.
OVERLEAF_OIDC_ISSUER(required)
OVERLEAF_OIDC_AUTHORIZATION_URL(required)
OVERLEAF_OIDC_TOKEN_URL(required)
OVERLEAF_OIDC_USER_INFO_URL(required)
OVERLEAF_OIDC_LOGOUT_URL(required)
The values of the following two required variables will be provided by the admin of your OP
OVERLEAF_OIDC_CLIENT_ID(required)
OVERLEAF_OIDC_CLIENT_SECRET(required)
OVERLEAF_OIDC_SCOPE
Default: openid profile email
OVERLEAF_OIDC_PROVIDER_ID
Arbitrary ID of the OP, defaults to oidc.
OVERLEAF_OIDC_PROVIDER_NAME
The name of the OP, used in the Linked Accounts section of the /user/settings page, defaults to OIDC Provider.
OVERLEAF_OIDC_IDENTITY_SERVICE_NAME
Display name for the identity service, used on the login page (default: Log in with $OVERLEAF_OIDC_PROVIDER_NAME).
OVERLEAF_OIDC_PROVIDER_DESCRIPTION
Description of OP, used in the Linked Accounts section (default: Log in with $OVERLEAF_OIDC_PROVIDER_NAME).
OVERLEAF_OIDC_PROVIDER_INFO_LINK
Learn more URL in the OP description, default: no Learn more link in the description.
OVERLEAF_OIDC_PROVIDER_HIDE_NOT_LINKED
Do not show OP on the /user/settings page, if the user’s account is not linked with the OP, default false.
OVERLEAF_OIDC_USER_ID_FIELD
The value of this attribute will be used by Overleaf as the external user ID, defaults to id. Other possible reasonable values are email and username (corresponding to preferred_username OIDC claim).
OVERLEAF_OIDC_ALLOWED_EMAIL_DOMAINS
Restricts Just-in-Time (JIT) account creation for users authenticating via OIDC. If set to a comma-separated list of domain names, a new account will be created only if the domain of the user’s email address matches one in the listed domains. If the domain does not match, an admin must manually create the user account using the OIDC user’s email address, with either a strong random password or, preferably, without the hashedPassword field at all. Domain names may include a leading *. wildcard to match subdomains.
Example: To allow JIT account creation for users with email address like name@example.com and name@math.example.com: OVERLEAF_OIDC_ALLOWED_EMAIL_DOMAINS=example.com, *.example.com
Example: To completely disable JIT account creation: OVERLEAF_OIDC_ALLOWED_EMAIL_DOMAINS=
OVERLEAF_OIDC_UPDATE_USER_DETAILS_ON_LOGIN
If set to true, updates the user first_name and last_name field on login, and disables the user details form on /user/settings page.
OVERLEAF_OIDC_IS_ADMIN_FIELD and OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE
When both environment variables are set, the login process updates user.isAdmin = true if the profile returned by the OP contains the attribute specified by OVERLEAF_OIDC_IS_ADMIN_FIELD and its value either matches OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE or is an array containing OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE (for example the groups claim), otherwise user.isAdmin is set to false. If OVERLEAF_OIDC_IS_ADMIN_FIELD is email then the value of the attribute emails[0].value is used for match checking.
The redirect URL for your OpenID Provider is https://my-overleaf-instance.com/oidc/login/callback.
Sample variables.env file
variables.env
OVERLEAF_APP_NAME="Our Overleaf Instance"ENABLED_LINKED_FILE_TYPES=project_file,project_output_file,url# Enables Thumbnail generation using ImageMagickENABLE_CONVERSIONS=true# Disables email confirmation requirementEMAIL_CONFIRMATION_DISABLED=true## Nginx# NGINX_WORKER_PROCESSES=4# NGINX_WORKER_CONNECTIONS=768## Set for TLS via nginx-proxy# OVERLEAF_BEHIND_PROXY=true# OVERLEAF_SECURE_COOKIE=trueOVERLEAF_SITE_URL=http://my-overleaf-instance.comOVERLEAF_NAV_TITLE=Our Overleaf Instance# OVERLEAF_HEADER_IMAGE_URL=http://somewhere.com/mylogo.pngOVERLEAF_ADMIN_EMAIL=support@example.comOVERLEAF_LEFT_FOOTER=[{"text": "Contact your support team", "url": "mailto:support@example.com"}]OVERLEAF_RIGHT_FOOTER=[{"text":"Hello, I am on the Right", "url":"https://github.com/yu-i-i/overleaf-cep"}]OVERLEAF_EMAIL_FROM_ADDRESS=team@example.comOVERLEAF_EMAIL_SMTP_HOST=smtp.example.comOVERLEAF_EMAIL_SMTP_PORT=587OVERLEAF_EMAIL_SMTP_SECURE=false# OVERLEAF_EMAIL_SMTP_USER=# OVERLEAF_EMAIL_SMTP_PASS=# OVERLEAF_EMAIL_SMTP_NAME=OVERLEAF_EMAIL_SMTP_LOGGER=falseOVERLEAF_EMAIL_SMTP_TLS_REJECT_UNAUTH=trueOVERLEAF_EMAIL_SMTP_IGNORE_TLS=falseOVERLEAF_CUSTOM_EMAIL_FOOTER=This system is run by department xOVERLEAF_PROXY_LEARN=trueNAV_HIDE_POWERED_BY=true################### OIDC for CE ###################EXTERNAL_AUTH=oidcOVERLEAF_OIDC_PROVIDER_ID=oidcOVERLEAF_OIDC_ISSUER=https://keycloak.provider.com/realms/exampleOVERLEAF_OIDC_AUTHORIZATION_URL=https://keycloak.provider.com/realms/example/protocol/openid-connect/authOVERLEAF_OIDC_TOKEN_URL=https://keycloak.provider.com/realms/example/protocol/openid-connect/tokenOVERLEAF_OIDC_USER_INFO_URL=https://keycloak.provider.com/realms/example/protocol/openid-connect/userinfoOVERLEAF_OIDC_LOGOUT_URL=https://keycloak.provider.com/realms/example/protocol/openid-connect/logoutOVERLEAF_OIDC_CLIENT_ID=Overleaf-OIDCOVERLEAF_OIDC_CLIENT_SECRET=DoNotUseThisATGgaAcTgCcATgGATTACAagGtTCaGcGTAGOVERLEAF_OIDC_IDENTITY_SERVICE_NAME='Log in with Keycloak OIDC Provider'OVERLEAF_OIDC_PROVIDER_NAME=OIDC Keycloak ProviderOVERLEAF_OIDC_PROVIDER_INFO_LINK=https://openid.netOVERLEAF_OIDC_IS_ADMIN_FIELD=emailOVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE=overleaf.admin@example.comOVERLEAF_OIDC_UPDATE_USER_DETAILS_ON_LOGIN=false
Step-by-step: goauthentik
This walks through a setup that is tested against goauthentik. Replace https://overleaf.example.com with your OVERLEAF_SITE_URL and https://authentik.example.com with the address of your Authentik.
1
Create the provider
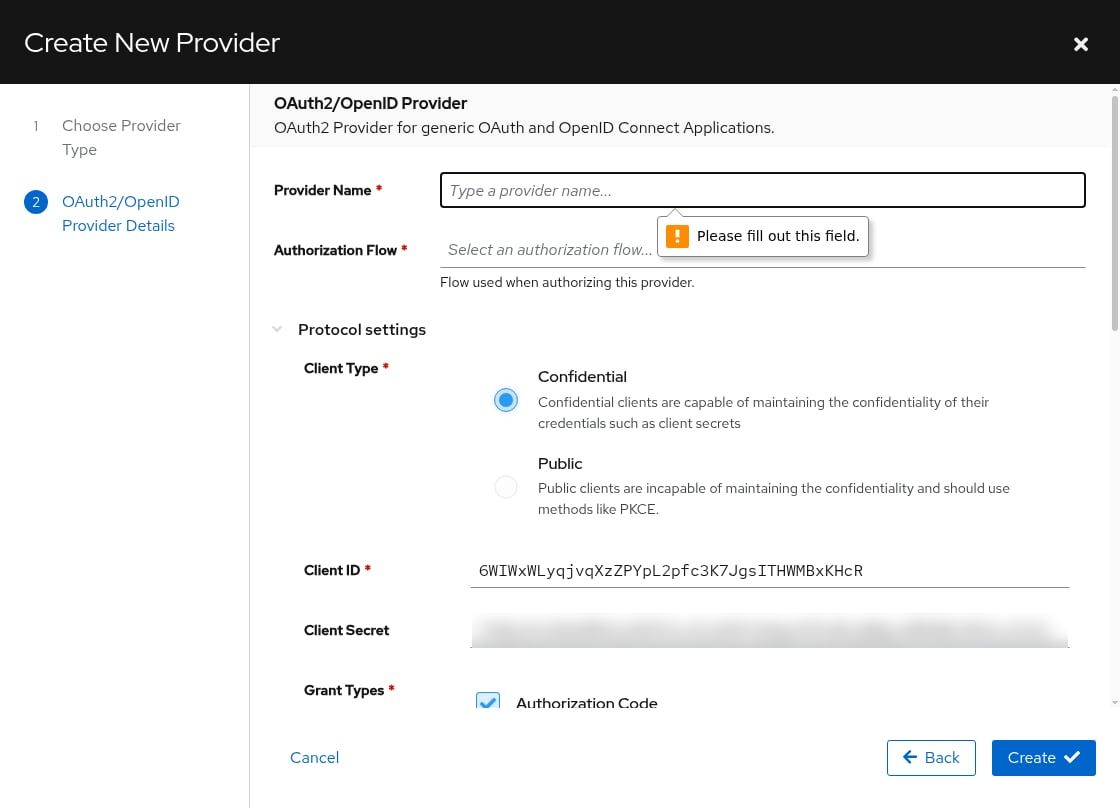
In Authentik, open Applications > Providers, click New Provider, choose OAuth2/OpenID Provider and click Next.
Client Type: Confidential.
Redirect URIs (under Protocol settings): add https://overleaf.example.com/oidc/login/callback with the matching mode Strict.
Copy Client ID and Client Secret now, into OVERLEAF_OIDC_CLIENT_ID and OVERLEAF_OIDC_CLIENT_SECRET.
Authentik: Client ID and Client Secret of a new provider
Authentik shows the client secret only while you create the provider. Later the edit form only offers Modify, which replaces the secret with a new one.
2
Create the application
Open Applications > Applications, create a new application, give it a name and a slug, for example overleaf, and select the provider. The slug becomes part of the issuer: https://authentik.example.com/application/o/overleaf/.
The admin flag is updated on every OIDC login. With a wrong field or value, every admin who logs in through OIDC loses the admin rights, including the admin created in the launchpad. Test the mapping with a second admin account first.
Tested variables.env for goauthentik
variables.env
EXTERNAL_AUTH=oidcOVERLEAF_OIDC_PROVIDER_ID=authentikOVERLEAF_OIDC_IDENTITY_SERVICE_NAME=Log in with AuthentikOVERLEAF_OIDC_ISSUER=https://authentik.example.com/application/o/overleaf/OVERLEAF_OIDC_AUTHORIZATION_URL=https://authentik.example.com/application/o/authorize/OVERLEAF_OIDC_TOKEN_URL=https://authentik.example.com/application/o/token/OVERLEAF_OIDC_USER_INFO_URL=https://authentik.example.com/application/o/userinfo/OVERLEAF_OIDC_LOGOUT_URL=https://authentik.example.com/application/o/overleaf/end-session/OVERLEAF_OIDC_CLIENT_ID=<Client ID>OVERLEAF_OIDC_CLIENT_SECRET=<Client Secret>OVERLEAF_OIDC_USER_ID_FIELD=usernameOVERLEAF_OIDC_IS_ADMIN_FIELD=groupsOVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE=AdminsOVERLEAF_OIDC_UPDATE_USER_DETAILS_ON_LOGIN=true
Q&A
The admin claim is set, but users do not become administrators
Answer: Check the following:
Version. Before v6.3.0, Overleaf did not read custom claims such as groups, so only OVERLEAF_OIDC_IS_ADMIN_FIELD=email worked. Upgrade to v6.3.0 or later.
The claim must be in the UserInfo response. Overleaf reads the claim from OVERLEAF_OIDC_USER_INFO_URL, not from the ID token. If your OP adds the claim only to the ID token, also add it to UserInfo, for example with Add to userinfo on a Keycloak mapper.
The value must match exactly, including case, for example Admins.
The admin status is checked again at every login: a user who was made an administrator in the admin panel loses it at the next login if the claim does not match.
Can I use GitHub as the OIDC provider?
Answer: No. GitHub supports OAuth 2.0 but not OpenID Connect for user login: it does not return an ID token, which Overleaf requires, so login fails with ID token not present in token response.To let users log in with their GitHub account, use an identity provider such as goauthentik or Keycloak, with GitHub as its login source, and connect Overleaf to that provider with OIDC.
Can I use GitLab as the OIDC provider?
Answer: Yes. GitLab, including self-managed GitLab, is an OpenID Connect provider. In GitLab, create an application under Applications (in your user, group or Admin area settings) with:
Then read the endpoints from https://gitlab.com/.well-known/openid-configuration, or from the same path on your GitLab, as described in Finding the values with the discovery document. For gitlab.com, the issuer is https://gitlab.com, without a trailing slash.
Login fails with "Unable to verify authorization request state" or "Invalid authorization request state"
Answer: Before redirecting to the OP, Overleaf stores a random state value in the user’s session, and checks it when the OP redirects back. These errors mean that the session at the callback is not the one that started the login.Unable to verify authorization request state means the browser did not send the session cookie back at the callback. Check that:
Users open Overleaf at the address of OVERLEAF_SITE_URL. The callback always goes to OVERLEAF_SITE_URL, so a login started from another address, such as http://192.168.1.20 while OVERLEAF_SITE_URL is https://overleaf.example.com, loses its session.
OVERLEAF_SECURE_COOKIE is not set when Overleaf is served over plain HTTP. Browsers drop secure cookies on HTTP. Any value enables it, including false, so remove the line instead.
Invalid authorization request state means a newer login replaced the stored value, for example after logging in from two tabs at once or going back in the browser during login. Close the other tabs and start the login again from the Overleaf login page.
Last modified on November 2, 2026
Was this page helpful?
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"Ayakaleaf Pro","description":"Overleaf Community Edition enhanced with all Pro features: open source, free to use, self-hostable.","colors":{"primary":"#0E0E0E","light":"#D4A27F","dark":"#0E0E0E"},"logo":{"light":"https://mintcdn.com/ayakaleaf-pro/JetHeEeglWIIXNds/logo/light.png?fit=max\u0026auto=format\u0026n=JetHeEeglWIIXNds\u0026q=85\u0026s=7f1abd8dcc74dd3b7cdafac9e6e82092","dark":"https://mintcdn.com/ayakaleaf-pro/JetHeEeglWIIXNds/logo/dark.png?fit=max\u0026auto=format\u0026n=JetHeEeglWIIXNds\u0026q=85\u0026s=4e369d29a8c5a6cd8b4b7697ddb1f7e2","href":"/"},"favicon":"https://mintcdn.com/ayakaleaf-pro/x9kfDjtWlyyhG_mR/favicon.png?fit=max\u0026auto=format\u0026n=x9kfDjtWlyyhG_mR\u0026q=85\u0026s=832c6bfafce5eb69ebc83783083a4a85","background":{"color":{"light":"#FDFDF7","dark":"#09090B"}},"navbar":{"links":[{"href":"https://github.com/ayaka-notes/ayakaleaf-pro-playground","label":"Playground"},{"href":"https://github.com/orgs/ayaka-notes/packages/container/package/overleaf-pro","label":"Docker Image"},{"href":"https://github.com/ayaka-notes/texlive-full","label":"TeXLive Full"}],"primary":{"type":"button","label":"Open GitHub","href":"https://github.com/ayaka-notes/ayakaleaf-pro"}},"footer":{"socials":{"github":"https://github.com/ayaka-notes"}},"styling":{"latex":true},"contextual":{"options":["copy","view","chatgpt","claude","perplexity","mcp","cursor","vscode","assistant","download-pdf","download-spec"],"display":"header"},"metadata":{"timestamp":true},"navigation":{"languages":[{"language":"en","default":true,"href":""},{"language":"zh-CN","href":"zh-CN"},{"language":"zh-TW","href":"zh-TW"},{"language":"ja","href":"ja"},{"language":"de","href":"de"},{"language":"fr","href":"fr"},{"language":"es","href":"es"},{"language":"it","href":"it"},{"language":"ko","href":"ko"},{"language":"ru","href":"ru"},{"language":"nl","href":"nl"},{"language":"pt","href":"pt"},{"language":"tr","href":"tr"},{"language":"uk","href":"uk"},{"language":"pl","href":"pl"},{"language":"cs","href":"cs"},{"language":"sv","href":"sv"},{"language":"fi","href":"fi"},{"language":"ar","href":"ar"},{"language":"vi","href":"vi"},{"language":"no","href":"no"},{"language":"da","href":"da"},{"language":"id","href":"id"},{"language":"zh-Hans","href":"zh-Hans"},{"language":"zh-Hant","href":"zh-Hant"}]}},"deployment":{"deploymentMetadataValue":{"subdomain":"ayakaleaf-pro","hasAudioNarration":false,"actualSubdomain":"ayakaleaf-pro","customDomains":[],"gitSource":{"type":"github","owner":"ayaka-notes","repo":"docs","deployBranch":"main","contentDirectory":"","isPrivate":false,"mountPath":"","label":""},"feedback":{"thumbs":true},"entitlements":{"AI_CHAT":{"status":"ENABLED"},"WEB_MCP":{"status":"ENABLED"},"NARRATION":{"status":"ENABLED"}},"buildId":"6b015084275034e27381e646","clientVersion":"0.0.4270","searchFilterCounts":[{"language":"en","tag":"On-Premises","count":159},{"language":"ar","tag":"الاستضافة المحلية","count":141},{"language":"cs","tag":"On-Premises","count":141},{"language":"da","tag":"On-premises","count":141},{"language":"de","tag":"On-Premises","count":141},{"language":"es","tag":"Local","count":141},{"language":"fi","tag":"Paikallinen asennus","count":141},{"language":"fr","tag":"Sur site","count":141},{"language":"id","tag":"On-Premises","count":141},{"language":"it","tag":"On-premise","count":141},{"language":"ja","tag":"オンプレミス","count":141},{"language":"ko","tag":"온프레미스","count":141},{"language":"nl","tag":"On-premises","count":141},{"language":"no","tag":"Lokal drift","count":141},{"language":"pl","tag":"On-Premises","count":141},{"language":"pt","tag":"On-Premises","count":141},{"language":"ru","tag":"Локальное развертывание","count":141},{"language":"sv","tag":"On-Premises","count":141},{"language":"tr","tag":"Şirket İçi Kurulum","count":141},{"language":"uk","tag":"Локальне розгортання","count":141},{"language":"vi","tag":"Tự triển khai (On-Premises)","count":141},{"language":"zh-CN","tag":"本地部署","count":141},{"language":"zh-Hans","tag":"本地部署","count":141},{"language":"zh-Hant","tag":"本地部署","count":141},{"language":"zh-TW","tag":"本地部署","count":141},{"language":"ar","tag":"الإعداد","count":66},{"language":"en","tag":"Configuration","count":66},{"language":"cs","tag":"Konfigurace","count":66},{"language":"da","tag":"Konfiguration","count":66},{"language":"de","tag":"Konfiguration","count":66},{"language":"es","tag":"Configuración","count":66},{"language":"fi","tag":"Määritys","count":66},{"language":"fr","tag":"Configuration","count":66},{"language":"id","tag":"Konfigurasi","count":66},{"language":"it","tag":"Configurazione","count":66},{"language":"ja","tag":"設定","count":66},{"language":"ko","tag":"구성","count":66},{"language":"nl","tag":"Configuratie","count":66},{"language":"no","tag":"Konfigurasjon","count":66},{"language":"pl","tag":"Konfiguracja","count":66},{"language":"pt","tag":"Configuração","count":66},{"language":"ru","tag":"Настройка","count":66},{"language":"sv","tag":"Konfiguration","count":66},{"language":"tr","tag":"Yapılandırma","count":66},{"language":"uk","tag":"Конфігурація","count":66},{"language":"vi","tag":"Cấu hình","count":66},{"language":"zh-CN","tag":"配置","count":66},{"language":"zh-Hans","tag":"配置","count":66},{"language":"zh-Hant","tag":"設定","count":66},{"language":"zh-TW","tag":"設定","count":66},{"language":"en","tag":"Developer","count":57},{"language":"ar","tag":"التثبيت","count":40},{"language":"en","tag":"Installation","count":40},{"language":"cs","tag":"Instalace","count":40},{"language":"da","tag":"Installation","count":40},{"language":"de","tag":"Installation","count":40},{"language":"es","tag":"Instalación","count":40},{"language":"fi","tag":"Asennus","count":40},{"language":"fr","tag":"Installation","count":40},{"language":"id","tag":"Instalasi","count":40},{"language":"it","tag":"Installazione","count":40},{"language":"ja","tag":"インストール","count":40},{"language":"ko","tag":"설치","count":40},{"language":"nl","tag":"Installatie","count":40},{"language":"no","tag":"Installasjon","count":40},{"language":"pl","tag":"Instalacja","count":40},{"language":"pt","tag":"Instalação","count":40},{"language":"ru","tag":"Установка","count":40},{"language":"sv","tag":"Installation","count":40},{"language":"tr","tag":"Kurulum","count":40},{"language":"uk","tag":"Встановлення","count":40},{"language":"vi","tag":"Cài đặt","count":40},{"language":"zh-CN","tag":"安装","count":40},{"language":"zh-Hans","tag":"安装","count":40},{"language":"zh-Hant","tag":"安裝","count":40},{"language":"zh-TW","tag":"安裝","count":40},{"language":"en","tag":"Data Model","count":37},{"language":"ar","tag":"Docker Compose","count":34},{"language":"en","tag":"Docker Compose","count":34},{"language":"cs","tag":"Docker Compose","count":34},{"language":"da","tag":"Docker Compose","count":34},{"language":"de","tag":"Docker Compose","count":34},{"language":"es","tag":"Docker Compose","count":34},{"language":"fi","tag":"Docker Compose","count":34},{"language":"fr","tag":"Docker Compose","count":34},{"language":"id","tag":"Docker Compose","count":34},{"language":"it","tag":"Docker Compose","count":34},{"language":"ja","tag":"Docker Compose","count":34},{"language":"ko","tag":"Docker Compose","count":34},{"language":"nl","tag":"Docker Compose","count":34},{"language":"no","tag":"Docker Compose","count":34},{"language":"pl","tag":"Docker Compose","count":34},{"language":"pt","tag":"Docker Compose","count":34},{"language":"ru","tag":"Docker Compose","count":34},{"language":"sv","tag":"Docker Compose","count":34},{"language":"tr","tag":"Docker Compose","count":34},{"language":"uk","tag":"Docker Compose","count":34},{"language":"vi","tag":"Docker Compose","count":34},{"language":"zh-CN","tag":"Docker Compose","count":34},{"language":"zh-Hans","tag":"Docker Compose","count":34},{"language":"zh-Hant","tag":"Docker Compose","count":34},{"language":"zh-TW","tag":"Docker Compose","count":34},{"language":"ar","tag":"Kubernetes","count":32},{"language":"en","tag":"Kubernetes","count":32},{"language":"cs","tag":"Kubernetes","count":32},{"language":"da","tag":"Kubernetes","count":32},{"language":"de","tag":"Kubernetes","count":32},{"language":"es","tag":"Kubernetes","count":32},{"language":"fi","tag":"Kubernetes","count":32},{"language":"fr","tag":"Kubernetes","count":32},{"language":"id","tag":"Kubernetes","count":32},{"language":"it","tag":"Kubernetes","count":32},{"language":"ja","tag":"Kubernetes","count":32},{"language":"ko","tag":"Kubernetes","count":32},{"language":"nl","tag":"Kubernetes","count":32},{"language":"no","tag":"Kubernetes","count":32},{"language":"pl","tag":"Kubernetes","count":32},{"language":"pt","tag":"Kubernetes","count":32},{"language":"ru","tag":"Kubernetes","count":32},{"language":"sv","tag":"Kubernetes","count":32},{"language":"tr","tag":"Kubernetes","count":32},{"language":"uk","tag":"Kubernetes","count":32},{"language":"vi","tag":"Kubernetes","count":32},{"language":"zh-CN","tag":"Kubernetes","count":32},{"language":"zh-Hans","tag":"Kubernetes","count":32},{"language":"zh-Hant","tag":"Kubernetes","count":32},{"language":"zh-TW","tag":"Kubernetes","count":32},{"language":"ar","tag":"استخدام Docker Compose","count":27},{"language":"en","tag":"Using Docker Compose","count":27},{"language":"cs","tag":"Použití Docker Compose","count":27},{"language":"da","tag":"Brug af Docker Compose","count":27},{"language":"de","tag":"Docker Compose verwenden","count":27},{"language":"es","tag":"Uso de Docker Compose","count":27},{"language":"fi","tag":"Docker Composen käyttö","count":27},{"language":"fr","tag":"Utiliser Docker Compose","count":27},{"language":"id","tag":"Menggunakan Docker Compose","count":27},{"language":"it","tag":"Utilizzo di Docker Compose","count":27},{"language":"ja","tag":"Docker Compose の使用","count":27},{"language":"ko","tag":"Docker Compose 사용","count":27},{"language":"nl","tag":"Docker Compose gebruiken","count":27},{"language":"no","tag":"Bruke Docker Compose","count":27},{"language":"pl","tag":"Korzystanie z Docker Compose","count":27},{"language":"pt","tag":"Usando o Docker Compose","count":27},{"language":"ru","tag":"Использование Docker Compose","count":27},{"language":"sv","tag":"Använda Docker Compose","count":27},{"language":"tr","tag":"Docker Compose kullanımı","count":27},{"language":"uk","tag":"Використання Docker Compose","count":27},{"language":"vi","tag":"Sử dụng Docker Compose","count":27},{"language":"zh-CN","tag":"使用 Docker Compose","count":27},{"language":"zh-Hans","tag":"使用 Docker Compose","count":27},{"language":"zh-Hant","tag":"使用 Docker Compose","count":27},{"language":"zh-TW","tag":"使用 Docker Compose","count":27},{"language":"ar","tag":"المطوّرون","count":24},{"language":"en","tag":"User guide","count":24},{"language":"cs","tag":"Vývojáři","count":24},{"language":"da","tag":"Udvikler","count":24},{"language":"de","tag":"Entwickler","count":24},{"language":"es","tag":"Desarrollador","count":24},{"language":"fi","tag":"Kehittäjä","count":24},{"language":"fr","tag":"Développeur","count":24},{"language":"id","tag":"Pengembang","count":24},{"language":"it","tag":"Sviluppatore","count":24},{"language":"ja","tag":"開発者","count":24},{"language":"ko","tag":"개발자","count":24},{"language":"nl","tag":"Ontwikkelaar","count":24},{"language":"no","tag":"Utvikler","count":24},{"language":"pl","tag":"Dla deweloperów","count":24},{"language":"pt","tag":"Desenvolvedor","count":24},{"language":"ru","tag":"Разработчикам","count":24},{"language":"sv","tag":"Utvecklare","count":24},{"language":"tr","tag":"Geliştirici","count":24},{"language":"uk","tag":"Розробникам","count":24},{"language":"vi","tag":"Nhà phát triển","count":24},{"language":"zh-CN","tag":"开发者","count":24},{"language":"zh-Hans","tag":"开发者","count":24},{"language":"zh-Hant","tag":"開發者","count":24},{"language":"zh-TW","tag":"開發者","count":24},{"language":"ar","tag":"التكاملات","count":22},{"language":"en","tag":"Integrations","count":22},{"language":"cs","tag":"Integrace","count":22},{"language":"da","tag":"Integrationer","count":22},{"language":"de","tag":"Integrationen","count":22},{"language":"es","tag":"Integraciones","count":22},{"language":"fi","tag":"Integraatiot","count":22},{"language":"fr","tag":"Intégrations","count":22},{"language":"id","tag":"Integrasi","count":22},{"language":"it","tag":"Integrazioni","count":22},{"language":"ja","tag":"連携","count":22},{"language":"ko","tag":"통합","count":22},{"language":"nl","tag":"Integraties","count":22},{"language":"no","tag":"Integrasjoner","count":22},{"language":"pl","tag":"Integracje","count":22},{"language":"pt","tag":"Integrações","count":22},{"language":"ru","tag":"Интеграции","count":22},{"language":"sv","tag":"Integrationer","count":22},{"language":"tr","tag":"Entegrasyonlar","count":22},{"language":"uk","tag":"Інтеграції","count":22},{"language":"vi","tag":"Tích hợp","count":22},{"language":"zh-CN","tag":"集成","count":22},{"language":"zh-Hans","tag":"集成","count":22},{"language":"zh-Hant","tag":"整合","count":22},{"language":"zh-TW","tag":"整合","count":22},{"language":"ar","tag":"المصادقة","count":14},{"language":"cs","tag":"Ověřování","count":14},{"language":"da","tag":"Godkendelse","count":14},{"language":"de","tag":"Authentifizierung","count":14},{"language":"es","tag":"Autenticación","count":14},{"language":"fi","tag":"Todennus","count":14},{"language":"fr","tag":"Authentification","count":14},{"language":"id","tag":"Autentikasi","count":14},{"language":"it","tag":"Autenticazione","count":14},{"language":"ja","tag":"認証","count":14},{"language":"ko","tag":"인증","count":14},{"language":"nl","tag":"Authenticatie","count":14},{"language":"no","tag":"Autentisering","count":14},{"language":"pl","tag":"Uwierzytelnianie","count":14},{"language":"pt","tag":"Autenticação","count":14},{"language":"ru","tag":"Аутентификация","count":14},{"language":"sv","tag":"Autentisering","count":14},{"language":"tr","tag":"Kimlik Doğrulama","count":14},{"language":"uk","tag":"Автентифікація","count":14},{"language":"vi","tag":"Xác thực","count":14},{"language":"zh-CN","tag":"身份验证","count":14},{"language":"zh-Hans","tag":"身份验证","count":14},{"language":"zh-Hant","tag":"身分驗證","count":14},{"language":"zh-TW","tag":"身分驗證","count":14},{"language":"ar","tag":"واجهات برمجة الخدمات","count":13},{"language":"cs","tag":"API služeb","count":13},{"language":"da","tag":"Tjeneste-API","count":13},{"language":"de","tag":"Service-API","count":13},{"language":"es","tag":"API de servicios","count":13},{"language":"fi","tag":"Palvelujen API","count":13},{"language":"fr","tag":"API des services","count":13},{"language":"id","tag":"API layanan","count":13},{"language":"it","tag":"API dei servizi","count":13},{"language":"ja","tag":"サービス API","count":13},{"language":"ko","tag":"서비스 API","count":13},{"language":"nl","tag":"Service-API","count":13},{"language":"no","tag":"Tjeneste-API","count":13},{"language":"pl","tag":"API usług","count":13},{"language":"pt","tag":"API dos serviços","count":13},{"language":"ru","tag":"API сервисов","count":13},{"language":"sv","tag":"Tjänste-API","count":13},{"language":"tr","tag":"Hizmet API'si","count":13},{"language":"uk","tag":"API сервісів","count":13},{"language":"vi","tag":"API dịch vụ","count":13},{"language":"zh-CN","tag":"服务 API","count":13},{"language":"zh-Hans","tag":"服务 API","count":13},{"language":"zh-Hant","tag":"服務 API","count":13},{"language":"zh-TW","tag":"服務 API","count":13}],"searchSettings":{"maxResults":6}},"assistantConfig":{"enableAskAiButton":false,"enableStarterQuestions":true,"enableContextualStarterQuestions":true,"enableAskAiSearchBar":true},"basePath":"","hasChatPermissions":true,"hasWebMcpPermissions":true,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-rbac-roles","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"rbac-expansion","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"site-roles","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-metadata","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-serve","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"live-agents","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"starter-pricing","enabled":true,"variant":{"name":"control","enabled":true,"payload":{"type":"string","value":"control"},"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"wildcard-email-auth","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[{"filePath":"style.css","content":"@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-Regular-Static.otf\") format(\"opentype\");font-weight:400;font-style:normal;font-display:swap}@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-RegularItalic-Static.otf\") format(\"opentype\");font-weight:400;font-style:italic;font-display:swap}@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-Medium-Static.otf\") format(\"opentype\");font-weight:500;font-style:normal;font-display:swap}@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-MediumItalic-Static.otf\") format(\"opentype\");font-weight:500;font-style:italic;font-display:swap}@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-Semibold-Static.otf\") format(\"opentype\");font-weight:600;font-style:normal;font-display:swap}@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-SemiboldItalic-Static.otf\") format(\"opentype\");font-weight:600;font-style:italic;font-display:swap}@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-Bold-Static.otf\") format(\"opentype\");font-weight:700;font-style:normal;font-display:swap}@font-face{font-family:\"Site Sans\";src:url(\"/fonts/SiteSans-Text-BoldItalic-Static.otf\") format(\"opentype\");font-weight:700;font-style:italic;font-display:swap}@font-face{font-family:\"Site Serif Display\";src:url(\"/fonts/SiteSerif-Display-Regular-Static.otf\") format(\"opentype\");font-weight:400;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif Display\";src:url(\"/fonts/SiteSerif-Display-RegularItalic-Static.otf\") format(\"opentype\");font-weight:400;font-style:italic;font-display:swap}@font-face{font-family:\"Site Serif Display\";src:url(\"/fonts/SiteSerif-Display-Medium-Static.otf\") format(\"opentype\");font-weight:500;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif Display\";src:url(\"/fonts/SiteSerif-Display-Semibold-Static.otf\") format(\"opentype\");font-weight:600;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif Display\";src:url(\"/fonts/SiteSerif-Display-Bold-Static.otf\") format(\"opentype\");font-weight:700;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-Regular-Static.otf\") format(\"opentype\");font-weight:400;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-RegularItalic-Static.otf\") format(\"opentype\");font-weight:400;font-style:italic;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-Medium-Static.otf\") format(\"opentype\");font-weight:500;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-MediumItalic-Static.otf\") format(\"opentype\");font-weight:500;font-style:italic;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-Semibold-Static.otf\") format(\"opentype\");font-weight:600;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-SemiboldItalic-Static.otf\") format(\"opentype\");font-weight:600;font-style:italic;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-Bold-Static.otf\") format(\"opentype\");font-weight:700;font-style:normal;font-display:swap}@font-face{font-family:\"Site Serif\";src:url(\"/fonts/SiteSerif-Text-BoldItalic-Static.otf\") format(\"opentype\");font-weight:700;font-style:italic;font-display:swap}:root{--always-white: 0 0% 100%;--always-black: 0 0% 0%;--constant-book-cloth: 15 55% 80%;--constant-clay: 15 60% 85%;--constant-kraft: 25 40% 83%;--constant-manilla: 40 20% 92%;--constant-slate-000: 0 0% 100%;--constant-slate-050: 48 33.3% 97.1%;--constant-slate-100: 53 28.6% 94.5%;--constant-slate-150: 48 25% 92.2%;--constant-slate-200: 50 20.7% 88.6%;--constant-slate-250: 51 16.5% 84.5%;--constant-slate-300: 50 11.5% 79.6%;--constant-slate-350: 50 9% 73.7%;--constant-slate-400: 49 6.5% 66.9%;--constant-slate-450: 48 4.8% 59.2%;--constant-slate-500: 53 3.2% 51.4%;--constant-slate-550: 51 3.1% 43.7%;--constant-slate-600: 48 2.7% 35.9%;--constant-slate-650: 48 3.4% 29.2%;--constant-slate-700: 60 2.5% 23.3%;--constant-slate-750: 60 2.1% 18.4%;--constant-slate-800: 60 2.7% 14.5%;--constant-slate-850: 30 3.3% 11.8%;--constant-slate-900: 30 4% 9.8%;--constant-slate-950: 60 2.6% 7.6%;--constant-slate-1000: 60 3.4% 5.7%}:root:not(.dark){--accent-brand: 15 63.1% 59.6%;--accent-main-000: 15 55.6% 52.4%;--accent-main-100: 15 55.6% 52.4%;--accent-main-200: 15 63.1% 59.6%;--accent-main-900: 0 0% 0%;--accent-pro-000: 251 34.2% 33.3%;--accent-pro-100: 251 40% 45.1%;--accent-pro-200: 251 61% 72.2%;--accent-pro-900: 253 33.3% 91.8%;--accent-secondary-000: 210 73.7% 40.2%;--accent-secondary-100: 210 70.9% 51.6%;--accent-secondary-200: 210 70.9% 51.6%;--accent-secondary-900: 211 72% 90%;--bg-000: 0 0% 100%;--bg-100: 48 33.3% 97.1%;--bg-200: 53 28.6% 94.5%;--bg-300: 48 25% 92.2%;--bg-400: 50 20.7% 88.6%;--bg-500: 50 20.7% 88.6%;--border-100: 30 3.3% 11.8%;--border-200: 30 3.3% 11.8%;--border-300: 30 3.3% 11.8%;--border-400: 30 3.3% 11.8%;--danger-000: 0 61.4% 22.4%;--danger-100: 0 58.6% 34.1%;--danger-200: 0 58.6% 34.1%;--danger-900: 0 50% 95%;--oncolor-100: 0 0% 100%;--oncolor-200: 60 6.7% 97.1%;--oncolor-300: 60 6.7% 97.1%;--text-000: 60 2.6% 7.6%;--text-100: 60 2.6% 7.6%;--text-200: 60 2.5% 23.3%;--text-300: 60 2.5% 23.3%;--text-400: 51 3.1% 43.7%;--text-500: 51 3.1% 43.7%}:root.dark{--accent-brand: 15 63.1% 59.6%;--accent-main-000: 15 55.6% 52.4%;--accent-main-100: 15 63.1% 59.6%;--accent-main-200: 15 63.1% 59.6%;--accent-main-900: 0 0% 0%;--accent-pro-000: 251 84.6% 74.5%;--accent-pro-100: 251 40.2% 54.1%;--accent-pro-200: 251 40% 45.1%;--accent-pro-900: 250 25.3% 19.4%;--accent-secondary-000: 210 71.1% 62%;--accent-secondary-100: 210 70.9% 51.6%;--accent-secondary-200: 210 70.9% 51.6%;--accent-secondary-900: 210 55.9% 24.6%;--bg-000: 60 2.1% 18.4%;--bg-100: 60 2.7% 14.5%;--bg-200: 30 3.3% 11.8%;--bg-300: 60 2.6% 7.6%;--bg-400: 60 3.4% 5.7%;--bg-500: 60 3.4% 5.7%;--border-100: 51 16.5% 84.5%;--border-200: 51 16.5% 84.5%;--border-300: 51 16.5% 84.5%;--border-400: 51 16.5% 84.5%;--danger-000: 0 73.1% 66.5%;--danger-100: 0 58.6% 34.1%;--danger-200: 0 58.6% 34.1%;--danger-900: 0 23% 15.6%;--oncolor-100: 0 0% 100%;--oncolor-200: 60 6.7% 97.1%;--oncolor-300: 60 6.7% 97.1%;--text-000: 48 33.3% 97.1%;--text-100: 48 33.3% 97.1%;--text-200: 50 9% 73.7%;--text-300: 50 9% 73.7%;--text-400: 48 4.8% 59.2%;--text-500: 48 4.8% 59.2%}#home-header{font-family:\"Site Sans\", system-ui, \"Segoe UI\", Roboto, Helvetica, Arial, sans-serif;font-weight:400!important;font-size:50px;line-height:1.2;margin-bottom:1rem;color:--text-000;display:flex;align-items:baseline;justify-content:center;flex-wrap:nowrap}#localization-select-trigger>:has(img[src*=\"flags\"]){display:none}div[id^=\"localization-select-item\"]>:has(img[src*=\"flags\"]){display:none}@media (min-width: 768px){#home-header{justify-content:center}}.build-with{font-family:\"Site Sans\", system-ui, \"Segoe UI\", Roboto, Helvetica, Arial, sans-serif;letter-spacing:-0.02em}.claude-wordmark-wrapper{display:inline-flex;align-items:baseline;margin-left:10px}.claude-wordmark{height:40px;width:auto;position:relative}.dark #home-header{color:white}.description-text{color:black}.dark .description-text{color:white}.dark .claude-wordmark{filter:invert(1)}:root{--bg-color: #f0efea}.dark{--bg-color: #2b2b2b}body,input,#category-select,.dropdown-item,#table-of-contents{font-family:\"Site Sans\", system-ui, \"Segoe UI\", Roboto, Helvetica, Arial, sans-serif}.eyebrow{font-family:\"Site Sans\", system-ui, \"Segoe UI\", Roboto, Helvetica, Arial, sans-serif;text-transform:uppercase;letter-spacing:0.02rem}#content-container{font-family:\"Site Sans\", system-ui, \"Segoe UI\", Roboto, Helvetica, Arial, sans-serif}#content-container h1,#content-container h2,#content-container h3,#content-container h4,#content-container h5,#content-container h6{font-family:\"Site Serif Display\", Georgia, \"Times New Roman\", Times, serif;font-weight:400;letter-spacing:0;word-spacing:0.1em}#content-container p{font-size:1rem;line-height:1.65rem}.font-extrabold{font-weight:600!important}.wide-table{width:100%;overflow-x:auto}.wide-table table{width:175%;margin-bottom:0}#prompt-library-container{margin:4rem auto;max-width:48rem;padding-left:1.25rem;padding-right:1.25rem}.prompt-library-title{font-size:24px;text-align:center;font-weight:700;color:#1f2937}.dark .prompt-library-title{color:#e5e7eb}.prompt-library-description{margin-top:1rem;text-align:center}.main-content{margin-bottom:10rem;max-width:64rem;margin-left:auto;margin-right:auto;padding-left:1.25rem;padding-right:1.25rem}.prompt-controllers{display:flex;gap:0.5rem}.prompt-search-container{position:relative;flex:1 1 0%}.prompt-search-icon-container{display:flex;position:absolute;top:0;bottom:0;left:0;align-items:center;padding-left:0.75rem}.prompt-search-icon{margin-left:0.25rem;margin-right:0.75rem;flex:none;width:1rem;height:1rem;background-color:#6b7280;mask-image:url(https://mintlify.b-cdn.net/v6.5.1/solid/magnifying-glass.svg);mask-repeat:no-repeat;mask-position:center center}input.prompt-search-bar{display:block;height:2.5rem;padding-left:2.5rem;border-radius:0.75rem;border-width:1px;background-color:#ffffff;width:100%;color:#111827;box-shadow:0 1px 2px 0 rgba(0, 0, 0, 0.05)}.dark input.prompt-search-bar{color:#ffffff;background-color:rgb(var(--background-dark));border-color:#d1d5db1a}input.prompt-search-bar:focus{outline-color:rgb(var(--primary))}.dark input.prompt-search-bar:focus{outline-color:rgb(var(--primary-light))}.dark .prompt-search-icon{background-color:#ffffff80}#category-select{padding-left:1rem;padding-right:2.5rem;height:2.5rem;display:flex;align-items:center;border-radius:0.75rem;border-width:1px;color:#111827;background-color:#ffffff;cursor:pointer;box-shadow:0 1px 2px 0 rgba(0, 0, 0, 0.05);white-space:nowrap}.dark #category-select{background-color:rgb(var(--background-dark));border-color:#d1d5db1a;color:#ffffff}#category-select:hover{background-color:#f9fafb}.dark #category-select:hover{background-color:#ffffff0d}#category-select:focus{outline-color:rgb(var(--primary))}.dark #category-select:focus{outline-color:rgb(var(--primary-light))}#categories-dropdown{top:calc(100% + 4px);padding:0.5rem 0.5rem;display:none;position:absolute;z-index:10;border-radius:0.75rem;border-width:1px;width:100%;color:#111827;background-color:#ffffff;box-shadow:0 1px 2px 0 rgba(0, 0, 0, 0.05)}.dark #categories-dropdown{background-color:rgb(var(--background-dark));border-color:#d1d5db1a;color:#ffffff}#categories-dropdown-clickout{position:fixed;top:0;right:0;bottom:0;left:0;z-index:0}.dropdown-icon-container{display:flex;position:absolute;top:0;bottom:0;right:0;align-items:center;padding-right:0.25rem}.dropdown-icon{margin-left:0.25rem;margin-right:0.75rem;flex:none;width:0.75rem;height:0.75rem;background-color:#6b7280;mask-image:url(https://mintlify.b-cdn.net/v6.5.1/solid/caret-down.svg);mask-repeat:no-repeat;mask-position:center center}.dark .dropdown-icon{background-color:#ffffff80}#prompts-container{grid-template-columns:repeat(1, minmax(0, 1fr));gap:2rem}.dropdown-item{padding:0.25rem 0.5rem;border-radius:0.375rem;display:flex;align-items:center;cursor:pointer}.dropdown-item:hover{background-color:#f9fafb}.dark .dropdown-item:hover{background-color:#ffffff0d}.check-icon{mask-image:url(https://mintlify.b-cdn.net/v6.5.1/solid/check.svg);height:0.875rem;width:1rem;background-color:rgb(var(--primary-light));mask-repeat:no-repeat;mask-position:center center}.prompt-card{margin:-0.75rem;padding:0.75rem;display:flex;border-radius:1rem}.prompt-card:hover{background-color:#03071208}.dark .prompt-card:hover{background-color:#ffffff08}.prompt-icon-container{display:flex;flex:none;align-items:center;justify-content:center;margin-right:1.5rem;border-radius:0.75rem;height:4rem;width:4rem;background-color:#cb785c1a}.prompt-icon{height:1.5rem;width:1.5rem;background-color:rgb(var(--primary-light));mask-repeat:no-repeat;mask-position:center center}.prompt-title{color:rgb(31 41 55);font-weight:600}.dark .prompt-title{color:rgb(229 231 235)}.prompt-description{margin-top:0.25rem}#prompts-container{display:grid;margin-top:2.5rem}@media (min-width: 640px){#category-select{width:16rem}}@media (min-width: 1024px){#prompts-container{grid-template-columns:repeat(2, minmax(0, 1fr))}}.home-cards-custom{display:grid;grid-template-columns:repeat(3, 1fr);grid-template-rows:repeat(2, auto);gap:1.5rem}.home-cards-custom .card{background:transparent;border:0.5px solid hsl(var(--border-300));border-radius:12px;padding:0.25rem}@media (max-width: 1024px){.home-cards-custom{grid-template-columns:repeat(2, 1fr);grid-template-rows:repeat(3, auto)}}@media (max-width: 768px){.home-cards-custom{grid-template-columns:1fr;grid-template-rows:repeat(6, auto)}}.relative{position:relative}.flex-1{flex:1 1 0%}.mermaid{position:relative;background-color:#FDFDFB;background-image:linear-gradient(rgba(235, 219, 188, .25) 1px, transparent 1px), /* Secondary color #EBDBBC with low opacity */\n linear-gradient(90deg, rgba(235, 219, 188, .25) 1px, transparent 1px),\n linear-gradient(rgba(235, 219, 188, .1) 1px, transparent 1px),\n linear-gradient(90deg, rgba(235, 219, 188, .1) 1px, transparent 1px);background-size:20px 20px,\n 20px 20px,\n 4px 4px,\n 4px 4px;background-position:-1px -1px,\n -1px -1px,\n -1px -1px,\n -1px -1px;padding:20px;border-radius:8px;border:1px solid rgba(235, 219, 188, .4);box-shadow:0 2px 4px rgba(64, 64, 62, 0.08)}.dark .mermaid{background-color:#1a1918;background-image:linear-gradient(rgba(212, 162, 127, .15) 1px, transparent 1px), /* Tertiary color #D4A27F with low opacity */\n linear-gradient(90deg, rgba(212, 162, 127, .15) 1px, transparent 1px),\n linear-gradient(rgba(212, 162, 127, .08) 1px, transparent 1px),\n linear-gradient(90deg, rgba(212, 162, 127, .08) 1px, transparent 1px);border:1px solid rgba(102, 102, 99, .5);box-shadow:0 2px 4px rgba(0, 0, 0, 0.2)}.digest-meta{display:flex;align-items:center;justify-content:space-between;flex-wrap:wrap;gap:0.5rem 1rem;padding:0.75rem 1rem;margin:1.5rem 0 2.5rem;border:1px solid hsl(var(--border-300) / 0.15);background:hsl(var(--bg-200));font-variant-numeric:tabular-nums;font-size:0.875rem;color:hsl(var(--text-400))}#content-container .digest-meta a{color:hsl(var(--accent-main-100));font-weight:500;text-decoration:none;border-bottom:none}#content-container .digest-meta a:hover{text-decoration:underline}.digest-feature{position:relative;margin:2.5rem 0;padding:1.875rem 1.875rem 1.625rem;background:radial-gradient(circle, hsl(var(--text-000) / 0.025) 1px, transparent 1px) 0 0 / 18px 18px,\n linear-gradient(180deg, hsl(var(--constant-manilla) / 0.55), hsl(var(--constant-manilla) / 0.38));border:1px solid hsl(var(--border-300) / 0.12);box-shadow:inset 0 1px 0 hsl(var(--text-000) / 0.04),\n 0 1px 2px hsl(var(--always-black) / 0.04)}.digest-feature::before{content:\"\";position:absolute;inset:0 auto 0 0;width:4px;background:hsl(var(--accent-brand))}.dark .digest-feature{background:radial-gradient(circle, hsl(var(--text-000) / 0.02) 1px, transparent 1px) 0 0 / 18px 18px,\n linear-gradient(180deg, hsl(var(--bg-000) / 0.75), hsl(var(--bg-000) / 0.5));border-color:hsl(var(--border-300) / 0.1);box-shadow:inset 0 1px 0 hsl(var(--text-000) / 0.03),\n 0 1px 2px hsl(var(--always-black) / 0.25)}.digest-feature>:first-child{margin-top:0}.digest-feature>:last-child{margin-bottom:0}.digest-feature-header{display:flex;align-items:center;flex-wrap:wrap;gap:0.625rem;margin:0 0 0.75rem}#content-container .digest-feature-title{font-family:\"Site Serif Display\", Georgia, serif;font-size:1.75rem;line-height:1.15;font-weight:500;letter-spacing:-0.015em;color:hsl(var(--text-000));margin:0}#content-container .digest-feature-pill{font-family:ui-monospace, \"SF Mono\", Menlo, Consolas, monospace;font-size:0.75rem;line-height:1;letter-spacing:0.01em;padding:0.3rem 0.6rem;border-radius:999px;background:hsl(var(--accent-brand) / 0.12);color:hsl(var(--accent-main-000));border:1px solid hsl(var(--accent-brand) / 0.25);white-space:nowrap;transform:translateY(1px)}#content-container .digest-feature-lede{font-size:1.0625rem;line-height:1.65;color:hsl(var(--text-100));margin:0 0 1.25rem;max-width:none}#content-container .digest-feature-lede code{font-size:0.875em;padding:0.1em 0.35em}#content-container .digest-feature-try{font-size:0.875rem;color:hsl(var(--text-400));margin:1.25rem 0 0.5rem}#content-container .digest-feature .frame{margin:1rem 0;border-radius:0;padding:0}#content-container .digest-feature .frame>*{border-radius:0}#content-container .digest-feature pre,#content-container .digest-feature [class*=\"CodeBlock\"]{border-radius:0}#content-container .digest-feature-link{display:inline-flex;align-items:center;gap:0.35rem;font-size:0.875rem;font-weight:500;color:hsl(var(--accent-main-100));text-decoration:none;border-bottom:none;margin-top:0.75rem}#content-container .digest-feature-link::after{content:\"→\";transition:transform 120ms ease-out}#content-container .digest-feature-link:hover::after{transform:translateX(3px)}.digest-wins{margin:2.5rem 0;padding:1.5rem 1.75rem 1.25rem;background:hsl(var(--bg-200));border:1px solid hsl(var(--border-300) / 0.1)}.dark .digest-wins{background:hsl(var(--bg-200) / 0.6)}#content-container .digest-wins-title{font-family:\"Site Serif Display\", Georgia, serif;font-size:1.25rem;font-weight:500;color:hsl(var(--text-000));margin:0 0 0.75rem}.digest-wins-grid{display:grid;grid-template-columns:repeat(auto-fit, minmax(16rem, 1fr));column-gap:2rem}#content-container .digest-wins-grid>div{position:relative;font-size:0.875rem;line-height:1.5;color:hsl(var(--text-300));padding:0.5rem 0 0.5rem 1.125rem;border-top:1px solid hsl(var(--border-300) / 0.06);margin:0}#content-container .digest-wins-grid>div::before{content:\"+\";position:absolute;left:0;top:0.5rem;font-family:ui-monospace, \"SF Mono\", Menlo, Consolas, monospace;font-size:0.8125rem;font-weight:600;color:hsl(var(--accent-brand))}#content-container .digest-wins-grid>div:first-child,#content-container .digest-wins-grid>div:nth-child(2){border-top:none;padding-top:0}#content-container .digest-wins-grid>div:first-child::before,#content-container .digest-wins-grid>div:nth-child(2)::before{top:0}#content-container .digest-wins-grid code{font-size:0.8125rem;padding:0.1em 0.3em}:root{--toc-wrapper-max: 92rem;--toc-wrapper-pad: 2rem;--toc-col: 19rem;--toc-side: 28rem;--toc-btn-size: 1.75rem}#toc-collapse-toggle{display:none;align-items:center;justify-content:center;position:fixed;top:10rem;right:calc(\n max((100% - var(--toc-wrapper-max)) / 2, 0px) + var(--toc-wrapper-pad) +\n var(--toc-col) - var(--toc-btn-size) - 0.35rem\n );transition:right 200ms ease-out;z-index:30;width:var(--toc-btn-size);height:var(--toc-btn-size);border-radius:9999px;border:1px solid hsl(var(--border-300) / 0.15);background:hsl(var(--bg-100));color:hsl(var(--text-400));cursor:pointer}#toc-collapse-toggle:hover{background:hsl(var(--bg-300));color:hsl(var(--text-100))}#toc-collapse-toggle svg{width:14px;height:14px;fill:none;stroke:currentColor;stroke-width:2.5;stroke-linecap:round;stroke-linejoin:round}#toc-collapse-toggle .toc-glyph{display:none;stroke-width:2}@media print{#toc-collapse-toggle{display:none!important}}@media (prefers-reduced-motion: reduce){#toc-collapse-toggle{transition:none}}@media (min-width: 1280px){html:has(#table-of-contents-layout) #toc-collapse-toggle{display:flex}html.toc-collapsed #toc-collapse-toggle .toc-chevron{transform:rotate(180deg)}html.toc-collapsed #toc-collapse-toggle{right:0.5rem;width:auto;padding:0 0.5rem;gap:0.25rem}html.toc-collapsed #toc-collapse-toggle .toc-glyph{display:block}html.toc-collapsed #table-of-contents-layout{display:none!important}html.toc-collapsed #content-side-layout:has(#table-of-contents-layout){display:none!important}html.toc-collapsed #content-container:has(#table-of-contents-layout) #content-area{width:100%!important}html.toc-collapsed #content-container:has(#table-of-contents-layout) #content-area>*{max-width:calc(var(--toc-wrapper-max) - var(--toc-side))}}@media (max-width: 640px){.digest-feature{padding:1.25rem 1rem 1rem;margin:1.5rem 0}#content-container .digest-feature-title{font-size:1.375rem}.digest-wins{padding:1.25rem 1rem 1rem}.digest-wins-grid{grid-template-columns:1fr}#content-container .digest-wins-grid>div:nth-child(2){border-top:1px solid hsl(var(--border-300) / 0.06);padding-top:0.5rem}#content-container .digest-wins-grid>div:nth-child(2)::before{top:0.5rem}}img[data-component-part=\"card-image\"]{aspect-ratio:16 / 9;height:auto;object-fit:cover;object-position:top center}"},{"filePath":"button.css","content":".btn{position:relative;display:inline-flex;gap:0.5rem;align-items:center;justify-content:center;flex-shrink:0;min-width:5rem;height:2.25rem;padding:0.5rem 1rem;white-space:nowrap;font-family:Styrene;font-weight:600;border-radius:0.5rem;\u0026:active{transform:scale(0.985)}\u0026.size-xs{height:1.75rem;min-width:3.5rem;padding:0 0.5rem;border-radius:0.25rem;font-size:0.75rem;gap:0.25rem}\u0026.size-sm{height:2rem;min-width:4rem;padding:0 0.75rem;border-radius:0.375rem;font-size:0.75rem}\u0026.size-lg{height:2.75rem;min-width:6rem;padding:0 1.25rem;border-radius:0.6rem}\u0026:disabled{pointer-events:none;opacity:0.5;box-shadow:none}\u0026:focus-visible{outline:none;--tw-ring-offset-shadow: var(--tw-ring-inset) 0 0 0 var(--tw-ring-offset-width) var(--tw-ring-offset-color);--tw-ring-shadow: var(--tw-ring-inset) 0 0 0 calc(1px + var(--tw-ring-offset-width)) var(--tw-ring-color);box-shadow:var(--tw-ring-offset-shadow), var(--tw-ring-shadow)}\u0026.primary{font-weight:600;color:hsl(var(--oncolor-100));background-color:hsl(var(--accent-main-100));background-image:linear-gradient(\n to right,\n hsl(var(--accent-main-100)) 0%,\n hsl(var(--accent-main-200) / 0.5) 50%,\n hsl(var(--accent-main-200)) 100%\n );background-size:200% 100%;background-position:0% 0%;border:0.5px solid hsl(var(--border-300) / 0.25);box-shadow:inset 0 0.5px 0px rgba(255, 255, 0, 0.15),\n 0 1px 1px rgba(0, 0, 0, 0.05);text-shadow:0 1px 2px rgb(0 0 0 / 10%);transition:all 150ms cubic-bezier(0.4, 0, 0.2, 1);\u0026:hover{background-position:100% 0%;background-image:linear-gradient(\n to right,\n hsl(var(--accent-main-200)) 0%,\n hsl(var(--accent-main-200)) 100%\n )}\u0026:active{background-color:hsl(var(--accent-main-000));box-shadow:inset 0 1px 6px rgba(0, 0, 0, 0.2);transform:scale(0.985)}}\u0026.flat{font-weight:500;color:hsl(var(--oncolor-100));background-color:hsl(var(--accent-main-100));transition:background-color 150ms;\u0026:hover{background-color:hsl(var(--accent-main-200))}}\u0026.secondary{font-weight:600;color:hsl(var(--text-100) / 0.9);background-image:radial-gradient(\n ellipse at center,\n hsl(var(--bg-500) / 0.1) 50%,\n hsl(var(--bg-500) / 0.3) 100%\n );border:0.5px solid hsl(var(--border-400));transition:color 150ms, background-color 150ms;\u0026:hover{color:hsl(var(--text-000));background-color:hsl(var(--bg-500) / 0.6)}\u0026:active{background-color:hsl(var(--bg-500) / 0.5)}}\u0026.outline{font-weight:600;color:hsl(var(--text-200));background-color:transparent;border:1.5px solid currentColor;transition:color 150ms, background-color 150ms;\u0026:hover{color:hsl(var(--text-100));background-color:hsl(var(--bg-400));border-color:hsl(var(--bg-400))}}\u0026.ghost{color:hsl(var(--text-200));border-color:transparent;transition:color 150ms, background-color 150ms;\u0026:hover{color:hsl(var(--text-100));background-color:hsl(var(--bg-500) / 0.4)}\u0026:active{background-color:hsl(var(--bg-400))}}\u0026.underline{opacity:0.8;text-decoration-line:none;text-underline-offset:3px;transition:all 150ms;\u0026:hover{opacity:1;text-decoration-line:underline}\u0026:active{transform:scale(0.985)}}\u0026.danger{font-weight:600;color:hsl(var(--oncolor-100));background-color:hsl(var(--danger-100));transition:background-color 150ms;\u0026:hover{background-color:hsl(var(--danger-200))}}}"}]}
{"page":{"pagePath":"on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","slug":"/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","pageMetadata":{"title":"OIDC Authentication","description":"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.","icon":"id-card-clip","href":"/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,br:`br`,code:`code`,li:`li`,p:`p`,pre:`pre`,span:`span`,strong:`strong`,tbody:`tbody`,td:`td`,th:`th`,thead:`thead`,tr:`tr`,ul:`ul`,..._provideComponents(),...props.components},{Accordion,CodeBlock,Frame,Heading,Info,OptimizedImage,Step,Steps,Table,Warning}=_components;if(!Accordion)_missingMdxReference(`Accordion`,true);if(!CodeBlock)_missingMdxReference(`CodeBlock`,true);if(!Frame)_missingMdxReference(`Frame`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Info)_missingMdxReference(`Info`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Table)_missingMdxReference(`Table`,true);if(!Warning)_missingMdxReference(`Warning`,true);return _jsxs(_Fragment,{children:[_jsx(Info,{children:_jsxs(_components.p,{children:[`This feature is developed by `,_jsx(_components.a,{href:`https://github.com/yu-i-i/overleaf-cep`,children:`yu-i-i/overleaf-cep`}),`. Here we offers some documents for your configuration.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`configuration`,children:`Configuration`}),`\n`,_jsxs(_components.p,{children:[`Internally, Overleaf OIDC module uses the `,_jsx(_components.a,{href:`https://github.com/jaredhanson/passport-openidconnect`,children:`passport-openidconnect`}),` library. If you are having issues configuring OpenID Connect, it is worth reading the README for `,_jsx(_components.code,{children:`passport-openidconnect`}),` to get a feel for the configuration it expects.`]}),`\n`,_jsxs(_components.p,{children:[`The environment variable `,_jsx(_components.code,{children:`EXTERNAL_AUTH`}),` is required to enable the OIDC authentication module. This environment variable specifies which external authentication methods are activated. The value of this variable is a list. If the list includes `,_jsx(_components.code,{children:`oidc`}),` then OIDC authentication will be activated.`]}),`\n`,_jsxs(_components.p,{children:[`For example: `,_jsx(_components.code,{children:`EXTERNAL_AUTH=ldap oidc`})]}),`\n`,_jsxs(_components.p,{children:[`When using the OIDC authentication method, a user is redirected to the Identity Provider (IdP) authentication site. If the IdP successfully authenticates the user, the Overleaf users database is checked for a record containing a `,_jsx(_components.code,{children:`thirdPartyIdentifiers`}),` field structured as follows:`]}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`8`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`8`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`thirdPartyIdentifiers: [`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:` {`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:` externalUserId: \"...\",`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:` externalData: null,`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:` providerId: \"...\"`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:` }`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`]`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})}),`\n`,_jsxs(_components.p,{children:[`The `,_jsx(_components.code,{children:`externalUserId`}),` must match the user ID in the profile returned by the IdP server (see the `,_jsx(_components.code,{children:`OVERLEAF_OIDC_USER_ID_FIELD`}),` environment variable), and `,_jsx(_components.code,{children:`providerId`}),` must match the ID of the OIDC provider (see the `,_jsx(_components.code,{children:`OVERLEAF_OIDC_PROVIDER_ID`}),`).`]}),`\n`,_jsx(_components.p,{children:`If no matching record is found, the database is searched for a user with the primary email address matching the email in the IdP user profile:`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`If such a user is found, the `,_jsx(_components.code,{children:`thirdPartyIdentifiers`}),` field is updated.`]}),`\n`,_jsxs(_components.li,{children:[`If no matching user is found and JIT account creation is not disabled, a new user is created with the email address and `,_jsx(_components.code,{children:`thirdPartyIdentifiers`}),` from the IdP profile.`]}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`In both cases, the user is said to be ‘linked’ to the external OIDC user. The user can be unlinked from the OIDC provider on the `,_jsx(_components.code,{children:`/user/settings`}),` page.`]}),`\n`,_jsx(Heading,{level:`4`,id:`finding-the-values-with-the-discovery-document`,children:`Finding the values with the discovery document`}),`\n`,_jsxs(_components.p,{children:[`Every OpenID Provider (OP) publishes a discovery document at `,_jsx(_components.code,{children:`\u003cissuer>/.well-known/openid-configuration`}),`. Copy the values from it instead of typing them by hand; one wrong character is enough to break the login.`]}),`\n`,_jsxs(Steps,{children:[_jsxs(Step,{title:`Find the discovery URL`,children:[_jsxs(_components.p,{children:[`Your OP shows it on the page of the client (provider) you created for Overleaf. In Authentik, open `,_jsx(_components.strong,{children:`Applications > Providers`}),`, select the provider and look for `,_jsx(_components.strong,{children:`OpenID Configuration URL`}),` and `,_jsx(_components.strong,{children:`OpenID Configuration Issuer`}),`:`]}),_jsx(Frame,{caption:`Authentik: the discovery URL and the issuer of a provider (test instance)`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-provider.png?fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=e3cb5603d959665472b53e39b58b2775`,alt:``,\"data-og-width\":`1280`,width:`1280`,\"data-og-height\":`633`,height:`633`,\"data-path\":`images/on-premises/oidc-authentik-provider.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-provider.png?w=280\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=72e4295d4c53b669d4d1c9b90eb47770 280w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-provider.png?w=560\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=12f07a03d5c535cc838ba288b71a9441 560w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-provider.png?w=840\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=f5730766a820ab9087c856e8bce22d00 840w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-provider.png?w=1100\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=ca956bbe3f692be264950285f20cb7ab 1100w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-provider.png?w=1650\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=3fea9441df117c6487c7a0d21bf97ac4 1650w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-provider.png?w=2500\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=27d7ea7f346907eea28ee0408f7c29e4 2500w`})}),_jsx(_components.p,{children:`The URL usually looks like this:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Keycloak: `,_jsx(_components.code,{children:`https://keycloak.example.com/realms/\u003crealm>/.well-known/openid-configuration`})]}),`\n`,_jsxs(_components.li,{children:[`Authentik: `,_jsx(_components.code,{children:`https://authentik.example.com/application/o/\u003capplication-slug>/.well-known/openid-configuration`})]}),`\n`]})]}),_jsxs(Step,{title:`Read the values`,children:[_jsx(_components.p,{children:`Open the URL in a browser, or run on the Overleaf server:`}),_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`2`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`curl`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -s`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` https://authentik.example.com/application/o/overleaf/.well-known/openid-configuration`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:` |`}),_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:` jq`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` '{issuer, authorization_endpoint, token_endpoint, userinfo_endpoint, end_session_endpoint}'`})]}),`\n`]})})}),_jsx(_components.p,{children:`The answer of Authentik looks like this:`}),_jsx(CodeBlock,{filename:``,numberOfLines:`7`,language:`json`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`json`,children:_jsxs(_components.code,{language:`json`,numberOfLines:`7`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`{`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#9CDCFE`},children:` \"issuer\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"https://authentik.example.com/application/o/overleaf/\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`,`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#9CDCFE`},children:` \"authorization_endpoint\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"https://authentik.example.com/application/o/authorize/\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`,`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#9CDCFE`},children:` \"token_endpoint\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"https://authentik.example.com/application/o/token/\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`,`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#9CDCFE`},children:` \"userinfo_endpoint\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"https://authentik.example.com/application/o/userinfo/\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`,`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#9CDCFE`},children:` \"end_session_endpoint\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"https://authentik.example.com/application/o/overleaf/end-session/\"`})]}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`}`})}),`\n`]})})}),_jsx(_components.p,{children:`Authentik also lists these URLs further down on the provider page:`}),_jsx(Frame,{caption:`Authentik: the endpoints of a provider (test instance)`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-endpoints.png?fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=55d130cbbbf27fd11aebafa1ab3f090c`,alt:``,\"data-og-width\":`1280`,width:`1280`,\"data-og-height\":`633`,height:`633`,\"data-path\":`images/on-premises/oidc-authentik-endpoints.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-endpoints.png?w=280\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=cecf482a3ad3ad6462ff556ff680457a 280w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-endpoints.png?w=560\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=aa6cd2f436a90e824bfb1fb1e11dc849 560w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-endpoints.png?w=840\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=c5738c5367f1ee4d9fbc250606e878dd 840w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-endpoints.png?w=1100\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=66cbf486e1dc5bc9317d83e6750487fa 1100w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-endpoints.png?w=1650\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=fa4b031d521b6f6bf6cda2c97b01ed90 1650w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-endpoints.png?w=2500\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=918077313b50659bc704cef6c8f2883a 2500w`})})]}),_jsxs(Step,{title:_jsxs(_Fragment,{children:[`Copy them into `,_jsx(_components.code,{children:`variables.env`})]}),children:[_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Field in the discovery document`}),_jsx(_components.th,{children:`Environment variable`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`issuer`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`OVERLEAF_OIDC_ISSUER`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`authorization_endpoint`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`OVERLEAF_OIDC_AUTHORIZATION_URL`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`token_endpoint`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`OVERLEAF_OIDC_TOKEN_URL`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`userinfo_endpoint`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`OVERLEAF_OIDC_USER_INFO_URL`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.code,{children:`end_session_endpoint`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`OVERLEAF_OIDC_LOGOUT_URL`})})]})]})]}),_jsx(CodeBlock,{filename:``,numberOfLines:`5`,language:`dotenv`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`dotenv`,children:_jsxs(_components.code,{language:`dotenv`,numberOfLines:`5`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_ISSUER`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/overleaf/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_AUTHORIZATION_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/authorize/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_TOKEN_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/token/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_USER_INFO_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/userinfo/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_LOGOUT_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/overleaf/end-session/`})]}),`\n`]})})})]}),_jsxs(Step,{title:`Check that Overleaf can reach the OP`,children:[_jsx(_components.p,{children:`Overleaf calls the token and userinfo endpoints from inside its container, so the OP must be reachable from there, not only from your browser:`}),_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`2`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`docker`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` exec`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` sharelatex`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` curl`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -sS`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -o`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` /dev/null`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` -w`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` \"%{http_code}\\\\n\"`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D7BA7D`},children:` \\\\`})]}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` https://authentik.example.com/application/o/overleaf/.well-known/openid-configuration`})}),`\n`]})})}),_jsxs(_components.p,{children:[`It should print `,_jsx(_components.code,{children:`200`}),`.`]})]})]}),`\n`,_jsxs(Warning,{children:[_jsxs(_components.p,{children:[`Copy `,_jsx(_components.code,{children:`issuer`}),` exactly, including the trailing slash. Overleaf compares it character by character with the issuer in the ID token; any difference makes every OIDC login fail with:`]}),_jsx(_components.p,{children:_jsx(_components.code,{children:`{\"message\":{\"message\":\"ID token not issued by expected OpenID provider.\"}}`})}),_jsxs(_components.p,{children:[`In Authentik the issuer belongs to the application (`,_jsx(_components.code,{children:`.../application/o/\u003capplication-slug>/`}),`). It is not the address of the Authentik server, although the authorize, token and userinfo URLs are shared by all applications.`]})]}),`\n`,_jsx(Heading,{level:`4`,id:`environment-variables`,children:`Environment Variables`}),`\n`,_jsxs(_components.p,{children:[`The values of the following five required variables can be found using `,_jsx(_components.code,{children:`.well-known/openid-configuration`}),` endpoint of your OpenID Provider (OP), see above.`]}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_ISSUER`}),` `,_jsx(`strong`,{children:`(required)`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_AUTHORIZATION_URL`}),` `,_jsx(`strong`,{children:`(required)`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_TOKEN_URL`}),` `,_jsx(`strong`,{children:`(required)`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_USER_INFO_URL`}),` `,_jsx(`strong`,{children:`(required)`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_LOGOUT_URL`}),` `,_jsx(`strong`,{children:`(required)`})]}),`\n`]}),`\n`,_jsx(_components.p,{children:`The values of the following two required variables will be provided by the admin of your OP`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_CLIENT_ID`}),` `,_jsx(`strong`,{children:`(required)`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_CLIENT_SECRET`}),` `,_jsx(`strong`,{children:`(required)`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_SCOPE`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Default: `,_jsx(_components.code,{children:`openid profile email`})]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_PROVIDER_ID`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Arbitrary ID of the OP, defaults to `,_jsx(_components.code,{children:`oidc`}),`.`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_PROVIDER_NAME`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`The name of the OP, used in the `,_jsx(_components.code,{children:`Linked Accounts`}),` section of the `,_jsx(_components.code,{children:`/user/settings`}),` page, defaults to `,_jsx(_components.code,{children:`OIDC Provider`}),`.`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_IDENTITY_SERVICE_NAME`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Display name for the identity service, used on the login page (default: `,_jsx(_components.code,{children:`Log in with $OVERLEAF_OIDC_PROVIDER_NAME`}),`).`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_PROVIDER_DESCRIPTION`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Description of OP, used in the `,_jsx(_components.code,{children:`Linked Accounts`}),` section (default: `,_jsx(_components.code,{children:`Log in with $OVERLEAF_OIDC_PROVIDER_NAME`}),`).`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_PROVIDER_INFO_LINK`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`Learn more`}),` URL in the OP description, default: no `,_jsx(_components.code,{children:`Learn more`}),` link in the description.`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_PROVIDER_HIDE_NOT_LINKED`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Do not show OP on the `,_jsx(_components.code,{children:`/user/settings`}),` page, if the user’s account is not linked with the OP, default `,_jsx(_components.code,{children:`false`}),`.`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_USER_ID_FIELD`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`The value of this attribute will be used by Overleaf as the external user ID, defaults to `,_jsx(_components.code,{children:`id`}),`. Other possible reasonable values are `,_jsx(_components.code,{children:`email`}),` and `,_jsx(_components.code,{children:`username`}),` (corresponding to `,_jsx(_components.code,{children:`preferred_username`}),` OIDC claim).`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_ALLOWED_EMAIL_DOMAINS`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Restricts Just-in-Time (JIT) account creation for users authenticating via OIDC. If set to a comma-separated list of domain names, a new account will be created only if the domain of the user’s email address matches one in the listed domains. If the domain does not match, an admin must manually create the user account using the OIDC user’s email address, with either a strong random password or, preferably, without the `,_jsx(_components.code,{children:`hashedPassword`}),` field at all. Domain names may include a leading `,_jsx(_components.code,{children:`*.`}),` wildcard to match subdomains.`,`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Example: To allow JIT account creation for users with email address like `,_jsx(_components.code,{children:`name@example.com`}),` and `,_jsx(_components.code,{children:`name@math.example.com`}),`:`,_jsx(_components.br,{}),`\n`,_jsx(_components.code,{children:`OVERLEAF_OIDC_ALLOWED_EMAIL_DOMAINS=example.com, *.example.com`})]}),`\n`,_jsxs(_components.li,{children:[`Example: To completely disable JIT account creation:`,_jsx(_components.br,{}),`\n`,_jsx(_components.code,{children:`OVERLEAF_OIDC_ALLOWED_EMAIL_DOMAINS=`})]}),`\n`]}),`\n`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_UPDATE_USER_DETAILS_ON_LOGIN`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`If set to `,_jsx(_components.code,{children:`true`}),`, updates the user `,_jsx(_components.code,{children:`first_name`}),` and `,_jsx(_components.code,{children:`last_name`}),` field on login, and disables the user details form on `,_jsx(_components.code,{children:`/user/settings`}),` page.`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_OIDC_IS_ADMIN_FIELD`}),` and `,_jsx(_components.code,{children:`OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`When both environment variables are set, the login process updates `,_jsx(_components.code,{children:`user.isAdmin = true`}),` if the profile returned by the OP contains the attribute specified by `,_jsx(_components.code,{children:`OVERLEAF_OIDC_IS_ADMIN_FIELD`}),` and its value either matches `,_jsx(_components.code,{children:`OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE`}),` or is an array containing `,_jsx(_components.code,{children:`OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE`}),` (for example the `,_jsx(_components.code,{children:`groups`}),` claim), otherwise `,_jsx(_components.code,{children:`user.isAdmin`}),` is set to `,_jsx(_components.code,{children:`false`}),`. If `,_jsx(_components.code,{children:`OVERLEAF_OIDC_IS_ADMIN_FIELD`}),` is `,_jsx(_components.code,{children:`email`}),` then the value of the attribute `,_jsx(_components.code,{children:`emails[0].value`}),` is used for match checking.`]}),`\n`]}),`\n`]}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`The redirect URL for your OpenID Provider is `,_jsx(_components.code,{children:`https://my-overleaf-instance.com/oidc/login/callback`}),`.`]}),`\n`,_jsx(Accordion,{title:`Sample variables.env file`,id:`sample-variables-env-file`,children:_jsx(CodeBlock,{filename:`variables.env`,wrap:`true`,numberOfLines:`61`,language:`dotenv`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`dotenv`,children:_jsxs(_components.code,{language:`dotenv`,numberOfLines:`61`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_APP_NAME`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"Our Overleaf Instance\"`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`ENABLED_LINKED_FILE_TYPES`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`project_file,project_output_file,url`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# Enables Thumbnail generation using ImageMagick`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`ENABLE_CONVERSIONS`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`true`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# Disables email confirmation requirement`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`EMAIL_CONFIRMATION_DISABLED`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`true`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`## Nginx`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# NGINX_WORKER_PROCESSES=4`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# NGINX_WORKER_CONNECTIONS=768`})}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`## Set for TLS via nginx-proxy`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# OVERLEAF_BEHIND_PROXY=true`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# OVERLEAF_SECURE_COOKIE=true`})}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_SITE_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`http://my-overleaf-instance.com`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_NAV_TITLE`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`Our Overleaf Instance`})]}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# OVERLEAF_HEADER_IMAGE_URL=http://somewhere.com/mylogo.png`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_ADMIN_EMAIL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`support@example.com`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_LEFT_FOOTER`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`[{`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"text\": \"Contact your support team\", \"url\": \"mailto:support@example.com\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`}]`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_RIGHT_FOOTER`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`[{`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`\"text\":\"Hello, I am on the Right\", \"url\":\"https://github.com/yu-i-i/overleaf-cep\"`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`}]`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_EMAIL_FROM_ADDRESS`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`team@example.com`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_EMAIL_SMTP_HOST`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`smtp.example.com`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_EMAIL_SMTP_PORT`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`587`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_EMAIL_SMTP_SECURE`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`false`})]}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# OVERLEAF_EMAIL_SMTP_USER=`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# OVERLEAF_EMAIL_SMTP_PASS=`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`# OVERLEAF_EMAIL_SMTP_NAME=`})}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_EMAIL_SMTP_LOGGER`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`false`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_EMAIL_SMTP_TLS_REJECT_UNAUTH`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`true`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_EMAIL_SMTP_IGNORE_TLS`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`false`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_CUSTOM_EMAIL_FOOTER`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`This system is run by department x`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_PROXY_LEARN`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`true`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`NAV_HIDE_POWERED_BY`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`true`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`#################`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`## OIDC for CE ##`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{style:{color:`#6E7781`,\"--shiki-dark\":`#6A9955`},children:`#################`})}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`EXTERNAL_AUTH`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`oidc`})]}),`\n`,_jsx(_components.span,{className:`line`}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_PROVIDER_ID`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`oidc`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_ISSUER`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://keycloak.provider.com/realms/example`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_AUTHORIZATION_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://keycloak.provider.com/realms/example/protocol/openid-connect/auth`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_TOKEN_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://keycloak.provider.com/realms/example/protocol/openid-connect/token`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_USER_INFO_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://keycloak.provider.com/realms/example/protocol/openid-connect/userinfo`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_LOGOUT_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://keycloak.provider.com/realms/example/protocol/openid-connect/logout`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_CLIENT_ID`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`Overleaf-OIDC`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_CLIENT_SECRET`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`DoNotUseThisATGgaAcTgCcATgGATTACAagGtTCaGcGTAG`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IDENTITY_SERVICE_NAME`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`'Log in with Keycloak OIDC Provider'`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_PROVIDER_NAME`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`OIDC Keycloak Provider`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_PROVIDER_INFO_LINK`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://openid.net`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IS_ADMIN_FIELD`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`email`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`overleaf.admin@example.com`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_UPDATE_USER_DETAILS_ON_LOGIN`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`false`})]}),`\n`]})})})}),`\n`,_jsx(Heading,{level:`2`,id:`step-by-step-goauthentik`,children:`Step-by-step: goauthentik`}),`\n`,_jsxs(_components.p,{children:[`This walks through a setup that is tested against `,_jsx(_components.a,{href:`https://goauthentik.io/`,children:`goauthentik`}),`. Replace `,_jsx(_components.code,{children:`https://overleaf.example.com`}),` with your `,_jsx(_components.code,{children:`OVERLEAF_SITE_URL`}),` and `,_jsx(_components.code,{children:`https://authentik.example.com`}),` with the address of your Authentik.`]}),`\n`,_jsxs(Steps,{children:[_jsxs(Step,{title:`Create the provider`,children:[_jsxs(_components.p,{children:[`In Authentik, open `,_jsx(_components.strong,{children:`Applications > Providers`}),`, click `,_jsx(_components.strong,{children:`New Provider`}),`, choose `,_jsx(_components.strong,{children:`OAuth2/OpenID Provider`}),` and click `,_jsx(_components.strong,{children:`Next`}),`.`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client Type`}),`: `,_jsx(_components.code,{children:`Confidential`}),`.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Redirect URIs`}),` (under `,_jsx(_components.strong,{children:`Protocol settings`}),`): add `,_jsx(_components.code,{children:`https://overleaf.example.com/oidc/login/callback`}),` with the matching mode `,_jsx(_components.code,{children:`Strict`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`Copy `,_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client Secret`}),` now, into `,_jsx(_components.code,{children:`OVERLEAF_OIDC_CLIENT_ID`}),` and `,_jsx(_components.code,{children:`OVERLEAF_OIDC_CLIENT_SECRET`}),`.`]}),`\n`]}),_jsx(Frame,{caption:`Authentik: Client ID and Client Secret of a new provider`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-create.png?fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=f127a92eaf3063714e9af515fe97c263`,alt:``,\"data-og-width\":`1120`,width:`1120`,\"data-og-height\":`808`,height:`808`,\"data-path\":`images/on-premises/oidc-authentik-create.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-create.png?w=280\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=63dc2dc463f593dc7b077a40658146c2 280w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-create.png?w=560\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=65c51099cab5f25aebe7d95e0dd7dd91 560w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-create.png?w=840\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=de6a2b447428b23ac3b5f44e7e3aba8d 840w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-create.png?w=1100\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=059a8e4a712d9459bd356dd8ab44ab92 1100w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-create.png?w=1650\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=f1bc366105f546840d0cba1baf17c44f 1650w, https://mintcdn.com/ayakaleaf-pro/TjqwH4XzxYAkHStq/images/on-premises/oidc-authentik-create.png?w=2500\u0026fit=max\u0026auto=format\u0026n=TjqwH4XzxYAkHStq\u0026q=85\u0026s=84230ae22ab4fec54737101b85e2d9b5 2500w`})}),_jsx(Warning,{children:_jsxs(_components.p,{children:[`Authentik shows the client secret only while you create the provider. Later the edit form only offers `,_jsx(_components.strong,{children:`Modify`}),`, which replaces the secret with a new one.`]})})]}),_jsx(Step,{title:`Create the application`,children:_jsxs(_components.p,{children:[`Open `,_jsx(_components.strong,{children:`Applications > Applications`}),`, create a new application, give it a name and a slug, for example `,_jsx(_components.code,{children:`overleaf`}),`, and select the provider. The slug becomes part of the issuer: `,_jsx(_components.code,{children:`https://authentik.example.com/application/o/overleaf/`}),`.`]})}),_jsx(Step,{title:`Copy the URLs`,children:_jsxs(_components.p,{children:[`Follow `,_jsx(_components.a,{href:`#finding-the-values-with-the-discovery-document`,children:`Finding the values with the discovery document`}),` above to fill in the five URLs.`]})}),_jsxs(Step,{title:`Map the admins (optional)`,children:[_jsxs(_components.p,{children:[`Authentik sends the user’s groups as the `,_jsx(_components.code,{children:`groups`}),` claim, an array. To make the members of the Authentik group `,_jsx(_components.code,{children:`Admins`}),` admins of Overleaf:`]}),_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`dotenv`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`dotenv`,children:_jsxs(_components.code,{language:`dotenv`,numberOfLines:`2`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IS_ADMIN_FIELD`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`groups`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`Admins`})]}),`\n`]})})}),_jsx(Warning,{children:_jsx(_components.p,{children:`The admin flag is updated on every OIDC login. With a wrong field or value, every admin who logs in through OIDC loses the admin rights, including the admin created in the launchpad. Test the mapping with a second admin account first.`})})]})]}),`\n`,_jsx(Accordion,{title:`Tested variables.env for goauthentik`,id:`tested-variables-env-for-goauthentik`,children:_jsx(CodeBlock,{filename:`variables.env`,wrap:`true`,numberOfLines:`14`,language:`dotenv`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`dotenv`,children:_jsxs(_components.code,{language:`dotenv`,numberOfLines:`14`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`EXTERNAL_AUTH`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`oidc`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_PROVIDER_ID`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`authentik`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IDENTITY_SERVICE_NAME`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`Log in with Authentik`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_ISSUER`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/overleaf/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_AUTHORIZATION_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/authorize/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_TOKEN_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/token/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_USER_INFO_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/userinfo/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_LOGOUT_URL`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`https://authentik.example.com/application/o/overleaf/end-session/`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_CLIENT_ID`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`\u003cClient ID>`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_CLIENT_SECRET`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`\u003cClient Secret>`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_USER_ID_FIELD`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`username`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IS_ADMIN_FIELD`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`groups`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_IS_ADMIN_FIELD_VALUE`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`Admins`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#9CDCFE`},children:`OVERLEAF_OIDC_UPDATE_USER_DETAILS_ON_LOGIN`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`true`})]}),`\n`]})})})}),`\n`,_jsx(Heading,{level:`3`,id:`q\u0026a`,children:`Q\u0026A`}),`\n`,_jsxs(Accordion,{title:`The admin claim is set, but users do not become administrators`,id:`the-admin-claim-is-set-but-users-do-not-become-administrators`,children:[_jsxs(_components.p,{children:[_jsx(`strong`,{children:`Answer:`}),` Check the following:`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(`strong`,{children:`Version.`}),` Before v6.3.0, Overleaf did not read custom claims such as `,_jsx(_components.code,{children:`groups`}),`, so only `,_jsx(_components.code,{children:`OVERLEAF_OIDC_IS_ADMIN_FIELD=email`}),` worked. Upgrade to v6.3.0 or later.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(`strong`,{children:`The claim must be in the UserInfo response.`}),` Overleaf reads the claim from `,_jsx(_components.code,{children:`OVERLEAF_OIDC_USER_INFO_URL`}),`, not from the ID token. If your OP adds the claim only to the ID token, also add it to UserInfo, for example with `,_jsx(_components.strong,{children:`Add to userinfo`}),` on a Keycloak mapper.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`The value must match exactly`}),`, including case, for example `,_jsx(_components.code,{children:`Admins`}),`.`]}),`\n`]}),_jsx(_components.p,{children:`The admin status is checked again at every login: a user who was made an administrator in the admin panel loses it at the next login if the claim does not match.`})]}),`\n`,_jsxs(Accordion,{title:`Can I use GitHub as the OIDC provider?`,id:`can-i-use-github-as-the-oidc-provider`,children:[_jsxs(_components.p,{children:[_jsx(`strong`,{children:`Answer:`}),` No. GitHub supports OAuth 2.0 but not OpenID Connect for user login: it does not return an ID token, which Overleaf requires, so login fails with `,_jsx(_components.code,{children:`ID token not present in token response`}),`.`]}),_jsxs(_components.p,{children:[`To let users log in with their GitHub account, use an identity provider such as `,_jsx(_components.a,{href:`/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication#step-by-step-goauthentik`,children:`goauthentik`}),` or Keycloak, with GitHub as its login source, and connect Overleaf to that provider with OIDC.`]})]}),`\n`,_jsxs(Accordion,{title:`Can I use GitLab as the OIDC provider?`,id:`can-i-use-gitlab-as-the-oidc-provider`,children:[_jsxs(_components.p,{children:[_jsx(`strong`,{children:`Answer:`}),` Yes. GitLab, including self-managed GitLab, is an OpenID Connect provider. In GitLab, create an application under `,_jsx(_components.strong,{children:`Applications`}),` (in your user, group or Admin area settings) with:`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Redirect URI`}),`: `,_jsx(_components.code,{children:`https://my-overleaf-instance.com/oidc/login/callback`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Scopes`}),`: `,_jsx(_components.code,{children:`openid`}),`, `,_jsx(_components.code,{children:`profile`}),` and `,_jsx(_components.code,{children:`email`})]}),`\n`]}),_jsxs(_components.p,{children:[`Then read the endpoints from `,_jsx(_components.code,{children:`https://gitlab.com/.well-known/openid-configuration`}),`, or from the same path on your GitLab, as described in `,_jsx(_components.a,{href:`/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication#finding-the-values-with-the-discovery-document`,children:`Finding the values with the discovery document`}),`. For `,_jsx(_components.code,{children:`gitlab.com`}),`, the issuer is `,_jsx(_components.code,{children:`https://gitlab.com`}),`, without a trailing slash.`]})]}),`\n`,_jsxs(Accordion,{title:`Login fails with \"Unable to verify authorization request state\" or \"Invalid authorization request state\"`,id:`login-fails-with-unable-to-verify-authorization-request-state-or-invalid-authorization-request-state`,children:[_jsxs(_components.p,{children:[_jsx(`strong`,{children:`Answer:`}),` Before redirecting to the OP, Overleaf stores a random `,_jsx(_components.code,{children:`state`}),` value in the user’s session, and checks it when the OP redirects back. These errors mean that the session at the callback is not the one that started the login.`]}),_jsxs(_components.p,{children:[_jsx(_components.code,{children:`Unable to verify authorization request state`}),` means the browser did not send the session cookie back at the callback. Check that:`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Users open Overleaf at the address of `,_jsx(_components.code,{children:`OVERLEAF_SITE_URL`}),`. The callback always goes to `,_jsx(_components.code,{children:`OVERLEAF_SITE_URL`}),`, so a login started from another address, such as `,_jsx(_components.code,{children:`http://192.168.1.20`}),` while `,_jsx(_components.code,{children:`OVERLEAF_SITE_URL`}),` is `,_jsx(_components.code,{children:`https://overleaf.example.com`}),`, loses its session.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.code,{children:`OVERLEAF_SECURE_COOKIE`}),` is not set when Overleaf is served over plain HTTP. Browsers drop secure cookies on HTTP. Any value enables it, including `,_jsx(_components.code,{children:`false`}),`, so remove the line instead.`]}),`\n`]}),_jsxs(_components.p,{children:[_jsx(_components.code,{children:`Invalid authorization request state`}),` means a newer login replaced the stored value, for example after logging in from two tabs at once or going back in the browser during login. Close the other tabs and start the login again from the Overleaf login page.`]})]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"config":{},"pageMetadata":{"title":"OIDC Authentication","description":"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.","icon":"id-card-clip","href":"/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"Configuration","slug":"configuration","depth":3,"children":[]},{"title":"Finding the values with the discovery document","slug":"finding-the-values-with-the-discovery-document","depth":4,"children":[]},{"title":"Environment Variables","slug":"environment-variables","depth":4,"children":[]},{"title":"Step-by-step: goauthentik","slug":"step-by-step-goauthentik","depth":2,"children":[{"title":"Q\u0026A","slug":"q\u0026a","depth":3,"children":[]}]}],"codeExamples":{}},"jsLinks":[],"subdomain":"ayakaleaf-pro","siteName":"Ayakaleaf Pro","title":"OIDC Authentication - Ayakaleaf Pro","contextualStarterQuestions":[{"_id":"6aeffa12601aeb1eca9e02b4","deploymentId":"6ab947b94ecd4e13d0332f05","questionText":"How do I enable OIDC auth?","status":"active","generatedBy":"contextual","path":"on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","createdAt":"2026-11-08T04:26:58.407Z","updatedAt":"2026-11-08T04:26:58.407Z","__v":0},{"_id":"6aeffa12601aeb1eca9e02b5","deploymentId":"6ab947b94ecd4e13d0332f05","questionText":"What is thirdPartyIdentifiers?","status":"active","generatedBy":"contextual","path":"on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","createdAt":"2026-11-08T04:26:58.407Z","updatedAt":"2026-11-08T04:26:58.407Z","__v":0},{"_id":"6aeffa12601aeb1eca9e02b6","deploymentId":"6ab947b94ecd4e13d0332f05","questionText":"How does user linking work?","status":"active","generatedBy":"contextual","path":"on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","createdAt":"2026-11-08T04:26:58.407Z","updatedAt":"2026-11-08T04:26:58.407Z","__v":0}],"navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{"en":{"href":"/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":0},"zh-CN":{"href":"/zh-CN/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"zh-TW":{"href":"/zh-TW/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"ja":{"href":"/ja/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"de":{"href":"/de/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"fr":{"href":"/fr/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"es":{"href":"/es/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"it":{"href":"/it/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"ko":{"href":"/ko/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"ru":{"href":"/ru/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"nl":{"href":"/nl/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"pt":{"href":"/pt/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"tr":{"href":"/tr/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"uk":{"href":"/uk/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"pl":{"href":"/pl/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"cs":{"href":"/cs/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"sv":{"href":"/sv/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"fi":{"href":"/fi/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"ar":{"href":"/ar/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"vi":{"href":"/vi/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"no":{"href":"/no/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"da":{"href":"/da/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"id":{"href":"/id/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"zh-Hans":{"href":"/zh-Hans/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1},"zh-Hant":{"href":"/zh-Hant/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication","matchLevel":1}}},"lastModified":"2026-11-02T16:11:45.732Z","gitLastModified":"2026-11-02T16:09:57.000Z","originalFileLocation":"on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication.mdx","locale":"en"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Ayakaleaf Pro\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"OIDC Authentication - Ayakaleaf Pro\">\u003cmeta data-mint-head property=\"og:description\" content=\"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Ayakaleaf Pro\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://ayakaleaf-pro.mintlify.site/_mintlify/api/og/v2?division=Authentication\u0026amp;title=OIDC+Authentication\u0026amp;description=Let+users+log+in+through+an+OpenID+Connect+provider%2C+with+a+step-by-step+goauthentik+example.\u0026amp;theme=a85f2ba202ff92d99974cf6c\u0026amp;signature=05fc9f4fc74b178e2a961390a7f33e62faa7e7ec49d675b24d7972812c62de91\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"OIDC Authentication - Ayakaleaf Pro\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://ayakaleaf-pro.mintlify.site/_mintlify/api/og/v2?division=Authentication\u0026amp;title=OIDC+Authentication\u0026amp;description=Let+users+log+in+through+an+OpenID+Connect+provider%2C+with+a+step-by-step+goauthentik+example.\u0026amp;theme=a85f2ba202ff92d99974cf6c\u0026amp;signature=05fc9f4fc74b178e2a961390a7f33e62faa7e7ec49d675b24d7972812c62de91\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/mintlify-assets/_mintlify/favicons/ayakaleaf-pro/o_LAbiVNKQm96Y75/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Ayakaleaf Pro\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#0E0E0E\">\u003clink data-mint-head rel=\"canonical\" href=\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication.md\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"en\" href=\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"zh-CN\" href=\"https://ayakaleaf-pro.mintlify.app/zh-CN/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"zh-TW\" href=\"https://ayakaleaf-pro.mintlify.app/zh-TW/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"ja\" href=\"https://ayakaleaf-pro.mintlify.app/ja/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"de\" href=\"https://ayakaleaf-pro.mintlify.app/de/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"fr\" href=\"https://ayakaleaf-pro.mintlify.app/fr/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"es\" href=\"https://ayakaleaf-pro.mintlify.app/es/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"it\" href=\"https://ayakaleaf-pro.mintlify.app/it/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"ko\" href=\"https://ayakaleaf-pro.mintlify.app/ko/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"ru\" href=\"https://ayakaleaf-pro.mintlify.app/ru/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"nl\" href=\"https://ayakaleaf-pro.mintlify.app/nl/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"pt\" href=\"https://ayakaleaf-pro.mintlify.app/pt/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"tr\" href=\"https://ayakaleaf-pro.mintlify.app/tr/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"uk\" href=\"https://ayakaleaf-pro.mintlify.app/uk/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"pl\" href=\"https://ayakaleaf-pro.mintlify.app/pl/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"cs\" href=\"https://ayakaleaf-pro.mintlify.app/cs/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"sv\" href=\"https://ayakaleaf-pro.mintlify.app/sv/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"fi\" href=\"https://ayakaleaf-pro.mintlify.app/fi/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"ar\" href=\"https://ayakaleaf-pro.mintlify.app/ar/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"vi\" href=\"https://ayakaleaf-pro.mintlify.app/vi/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"no\" href=\"https://ayakaleaf-pro.mintlify.app/no/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"da\" href=\"https://ayakaleaf-pro.mintlify.app/da/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"id\" href=\"https://ayakaleaf-pro.mintlify.app/id/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"zh-Hans\" href=\"https://ayakaleaf-pro.mintlify.app/zh-Hans/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"zh-Hant\" href=\"https://ayakaleaf-pro.mintlify.app/zh-Hant/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"x-default\" href=\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://ayakaleaf-pro.mintlify.app/#organization\",\"name\":\"Ayakaleaf Pro\",\"url\":\"https://ayakaleaf-pro.mintlify.app\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/ayakaleaf-pro/JetHeEeglWIIXNds/logo/light.png?fit=max\u0026auto=format\u0026n=JetHeEeglWIIXNds\u0026q=85\u0026s=7f1abd8dcc74dd3b7cdafac9e6e82092\"}},{\"@type\":\"WebSite\",\"@id\":\"https://ayakaleaf-pro.mintlify.app#website\",\"name\":\"Ayakaleaf Pro\",\"url\":\"https://ayakaleaf-pro.mintlify.app\",\"publisher\":{\"@id\":\"https://ayakaleaf-pro.mintlify.app/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication#webpage\",\"url\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\",\"name\":\"OIDC Authentication\",\"description\":\"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.\",\"dateModified\":\"2026-11-02T16:09:57.000Z\",\"isPartOf\":{\"@id\":\"https://ayakaleaf-pro.mintlify.app#website\"},\"breadcrumb\":{\"@id\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Configuration\",\"item\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/files-and-locations\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Docker Compose\",\"item\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit\"},{\"@type\":\"ListItem\",\"position\":3,\"name\":\"Authentication\",\"item\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication\"},{\"@type\":\"ListItem\",\"position\":4,\"name\":\"OIDC Authentication\",\"item\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication#article\",\"headline\":\"OIDC Authentication\",\"name\":\"OIDC Authentication\",\"description\":\"Let users log in through an OpenID Connect provider, with a step-by-step goauthentik example.\",\"url\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication\",\"mainEntityOfPage\":{\"@id\":\"https://ayakaleaf-pro.mintlify.app/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication#webpage\"},\"dateModified\":\"2026-11-02T16:09:57.000Z\",\"publisher\":{\"@id\":\"https://ayakaleaf-pro.mintlify.app/#organization\"},\"isPartOf\":{\"@id\":\"https://ayakaleaf-pro.mintlify.app#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Ayakaleaf Pro\",\"publisher\":{\"@type\":\"Organization\",\"name\":\"Ayakaleaf Pro\"},\"provider\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","agentPointerHref":"/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication.md","siteName":"Ayakaleaf Pro","nav":{"global":null,"languages":[{"language":"en","default":true,"tabs":[{"tab":"Home","icon":"house-chimney","pages":[{"title":"Home","href":""}]},{"tab":"On-Premises","icon":"server","groups":[{"group":"Overview","pages":[{"group":"Welcome","icon":"hand-wave","root":{"title":"Welcome","icon":"hand-wave","href":"/on-premises"},"pages":[{"title":"Features and Copyright","icon":"layer-plus","href":"/on-premises/readme/features-and-copyright"},{"title":"Trust and Security","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/expeditedssl.svg","href":"/on-premises/readme/trust-and-security"},{"title":"Overleaf Server Pro vs. Ayakaleaf Pro","icon":"scale-balanced","href":"/on-premises/readme/ayakaleaf-pro-vs-server-pro"},{"title":"Question and Answer","icon":"comment-question","href":"/on-premises/readme/question-and-answer"}]},{"group":"Release notes","icon":"code-branch","root":{"title":"Release notes","icon":"code-branch","href":"/on-premises/release-notes/index"},"pages":[{"title":"Release notes 6.x.x","href":"/on-premises/release-notes/release-notes-6.x.x"}]}]},{"group":"Installation","pages":[{"title":"Introduction","icon":"map-location","href":"/on-premises/installation/introduction"},{"group":"Using Docker Compose","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/docker.svg","root":{"title":"Using Docker Compose","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/docker.svg","href":"/on-premises/installation/using-docker-compose/index"},"pages":[{"group":"Linux","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/linux.svg","root":{"title":"Linux","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/linux.svg","href":"/on-premises/installation/using-docker-compose/linux/index"},"pages":[{"title":"0. Setup Docker","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/docker.svg","href":"/on-premises/installation/using-docker-compose/linux/0.-setup-docker"},{"title":"1. Download the Toolkit","icon":"arrow-down-to-bracket","href":"/on-premises/installation/using-docker-compose/linux/1.-download-the-toolkit"},{"title":"2. Familiarize yourself with the Toolkit","icon":"magnifying-glass","href":"/on-premises/installation/using-docker-compose/linux/2.-familiarize-yourself-with-the-toolkit"},{"title":"3. Initialize the configuration","icon":"circle-play","href":"/on-premises/installation/using-docker-compose/linux/3.-initialize-the-configuration"},{"title":"4. Get Ayakaleaf Pro Images","icon":"split","href":"/on-premises/installation/using-docker-compose/linux/4.-get-overleaf-pro-images"},{"title":"5. Personalizing your instance","icon":"square-sliders","href":"/on-premises/installation/using-docker-compose/linux/5.-personalizing-your-instance"},{"title":"6. Post-installation tasks","icon":"ballot-check","href":"/on-premises/installation/using-docker-compose/linux/6.-post-installation-tasks"}]},{"group":"macOS","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/apple.svg","root":{"title":"macOS","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/apple.svg","href":"/on-premises/installation/using-docker-compose/macos/index"},"pages":[{"title":"0. Setup Docker Desktop","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/docker.svg","href":"/on-premises/installation/using-docker-compose/macos/0.-setup-docker-desktop"},{"title":"1. Download the Toolkit","icon":"arrow-down-to-bracket","href":"/on-premises/installation/using-docker-compose/macos/1.-download-the-toolkit"},{"title":"2. Familiarize yourself with the Toolkit","icon":"magnifying-glass","href":"/on-premises/installation/using-docker-compose/macos/2.-familiarize-yourself-with-the-toolkit"},{"title":"3. Initialize the configuration","icon":"circle-play","href":"/on-premises/installation/using-docker-compose/macos/3.-initialize-the-configuration"},{"title":"4. Get Ayakaleaf Pro Images","icon":"split","href":"/on-premises/installation/using-docker-compose/macos/4.-get-ayakaleaf-pro-images"},{"title":"5. Personalizing your instance","icon":"square-sliders","href":"/on-premises/installation/using-docker-compose/macos/5.-personalizing-your-instance"},{"title":"6. Post-installation tasks","icon":"ballot-check","href":"/on-premises/installation/using-docker-compose/macos/6.-post-installation-tasks"},{"title":"Troubleshooting","icon":"screwdriver-wrench","href":"/on-premises/installation/using-docker-compose/macos/troubleshooting"}]},{"group":"Windows","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/windows.svg","root":{"title":"Windows","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/windows.svg","href":"/on-premises/installation/using-docker-compose/windows/index"},"pages":[{"title":"0. Setup WSL 2 and Docker Desktop","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/docker.svg","href":"/on-premises/installation/using-docker-compose/windows/0.-setup-wsl-and-docker-desktop"},{"title":"1. Download the Toolkit","icon":"arrow-down-to-bracket","href":"/on-premises/installation/using-docker-compose/windows/1.-download-the-toolkit"},{"title":"2. Familiarize yourself with the Toolkit","icon":"magnifying-glass","href":"/on-premises/installation/using-docker-compose/windows/2.-familiarize-yourself-with-the-toolkit"},{"title":"3. Initialize the configuration","icon":"circle-play","href":"/on-premises/installation/using-docker-compose/windows/3.-initialize-the-configuration"},{"title":"4. Get Ayakaleaf Pro Images","icon":"split","href":"/on-premises/installation/using-docker-compose/windows/4.-get-ayakaleaf-pro-images"},{"title":"5. Personalizing your instance","icon":"square-sliders","href":"/on-premises/installation/using-docker-compose/windows/5.-personalizing-your-instance"},{"title":"6. Post-installation tasks","icon":"ballot-check","href":"/on-premises/installation/using-docker-compose/windows/6.-post-installation-tasks"},{"title":"Troubleshooting","icon":"wrench","href":"/on-premises/installation/using-docker-compose/windows/troubleshooting"}]}]},{"group":"Using Kubernetes","icon":"dharmachakra","root":{"title":"Using Kubernetes","icon":"dharmachakra","href":"/on-premises/installation/using-kubernetes/index"},"pages":[{"title":"0. Prepare the nodes","icon":"server","href":"/on-premises/installation/using-kubernetes/0.-prepare-the-nodes"},{"title":"1. Get Ayakaleaf Pro Images","icon":"split","href":"/on-premises/installation/using-kubernetes/1.-get-ayakaleaf-pro-images"},{"title":"2. Create the namespace and secrets","icon":"key","href":"/on-premises/installation/using-kubernetes/2.-create-the-namespace-and-secrets"},{"title":"3. Deploy MongoDB and Redis","icon":"database","href":"/on-premises/installation/using-kubernetes/3.-deploy-mongodb-and-redis"},{"title":"4. Personalizing your instance","icon":"square-sliders","href":"/on-premises/installation/using-kubernetes/4.-personalizing-your-instance"},{"title":"5. Deploy Ayakaleaf Pro","icon":"rocket-launch","href":"/on-premises/installation/using-kubernetes/5.-deploy-ayakaleaf-pro"},{"title":"6. Post-installation tasks","icon":"ballot-check","href":"/on-premises/installation/using-kubernetes/6.-post-installation-tasks"}]},{"title":"Using Claude or Codex","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/claude.svg","href":"/on-premises/installation/using-claude-or-codex"},{"title":"Using GitHub Codespace","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/github.svg","href":"/on-premises/installation/using-the-github-codespace"},{"title":"Air-gapped/offline deployments","icon":"block-brick","href":"/on-premises/installation/air-gapped-offline-deployments"},{"title":"Migrate from Existing","icon":"u-turn-up-right","href":"/on-premises/installation/migrate-from-existing"}]},{"group":"Configuration","pages":[{"group":"Docker Compose","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/docker.svg","root":{"title":"Docker Compose","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/docker.svg","href":"/on-premises/configuration/overleaf-toolkit/index"},"pages":[{"title":"Files and locations","icon":"folder-open","href":"/on-premises/configuration/overleaf-toolkit/files-and-locations"},{"title":"Toolkit settings","icon":"gear-complex","href":"/on-premises/configuration/overleaf-toolkit/toolkit-settings"},{"title":"Environment variables","icon":"seedling","href":"/on-premises/configuration/overleaf-toolkit/environment-variables"},{"group":"Authentication","icon":"address-card","root":{"title":"Authentication","icon":"address-card","description":null,"href":"/on-premises/configuration/overleaf-toolkit/authentication/index"},"pages":[{"title":"OIDC Authentication","icon":"id-card-clip","href":"/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"},{"title":"SAML Authentication","description":"Let users log in through a SAML 2.0 identity provider, with a step-by-step goauthentik example.","icon":"key","href":"/on-premises/configuration/overleaf-toolkit/authentication/saml-authentication"},{"title":"LDAP Authentication","icon":"lock","href":"/on-premises/configuration/overleaf-toolkit/authentication/ldap-authentication"},{"title":"Public Access","icon":"lock-open","href":"/on-premises/configuration/overleaf-toolkit/authentication/public-access"},{"title":"reCAPTCHA","icon":"robot","href":"/on-premises/configuration/overleaf-toolkit/authentication/recaptcha"},{"title":"Password restrictions","icon":"key","href":"/on-premises/configuration/overleaf-toolkit/authentication/password-restrictions"}]},{"title":"Sandboxed Compiles","icon":"gear-code","href":"/on-premises/configuration/overleaf-toolkit/sandboxed-compiles"},{"title":"Pandoc Import and Export","icon":"file-lines","href":"/on-premises/configuration/overleaf-toolkit/pandoc-import-and-export"},{"group":"Integrations","icon":"puzzle-piece","root":{"title":"Integrations","icon":"puzzle-piece","href":"/on-premises/configuration/overleaf-toolkit/integrations/index"},"pages":[{"title":"Git integration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/git-alt.svg","href":"/on-premises/configuration/overleaf-toolkit/integrations/git-integration"},{"title":"GitHub Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/github.svg","href":"/on-premises/configuration/overleaf-toolkit/integrations/github-synchronisation"},{"title":"GitLab Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/gitlab.svg","href":"/on-premises/configuration/overleaf-toolkit/integrations/gitlab-synchronisation"},{"title":"Gitea Synchronisation","icon":"mug-hot","href":"/on-premises/configuration/overleaf-toolkit/integrations/gitea-synchronisation"},{"title":"Dropbox Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/dropbox.svg","href":"/on-premises/configuration/overleaf-toolkit/integrations/dropbox-synchronisation"},{"title":"Zotero Integration","icon":"z","href":"/on-premises/configuration/overleaf-toolkit/integrations/zotero-integration"},{"title":"Mendeley Integration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/mendeley.svg","href":"/on-premises/configuration/overleaf-toolkit/integrations/mendeley-integration"},{"title":"MCP Server","icon":"plug","href":"/on-premises/configuration/overleaf-toolkit/integrations/mcp-server"},{"title":"AI Integration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/openai.svg","href":"/on-premises/configuration/overleaf-toolkit/integrations/ai-integration"},{"title":"Overleaf Import API","icon":"rectangle-api","href":"/on-premises/configuration/overleaf-toolkit/integrations/overleaf-import-api"}]},{"title":"Templates","icon":"paste","href":"/on-premises/configuration/overleaf-toolkit/templates"},{"title":"External URL","icon":"link","href":"/on-premises/configuration/overleaf-toolkit/external-url"},{"title":"Logging","icon":"memo-circle-info","href":"/on-premises/configuration/overleaf-toolkit/logging"},{"title":"TLS proxy","icon":"lock","href":"/on-premises/configuration/overleaf-toolkit/tls-proxy"},{"title":"Branding","icon":"copyright","href":"/on-premises/configuration/overleaf-toolkit/branding"},{"title":"Localization","icon":"globe-pointer","href":"/on-premises/configuration/overleaf-toolkit/localization"},{"title":"Email delivery","icon":"paper-plane-top","href":"/on-premises/configuration/overleaf-toolkit/email-delivery"},{"title":"Redis","icon":"memory","href":"/on-premises/configuration/overleaf-toolkit/redis"},{"title":"S3","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/aws.svg","href":"/on-premises/configuration/overleaf-toolkit/s3"},{"title":"Adding LaTeX user help","icon":"graduation-cap","href":"/on-premises/configuration/overleaf-toolkit/adding-latex-user-help"}]},{"group":"Kubernetes","icon":"dharmachakra","root":{"title":"Kubernetes","icon":"dharmachakra","href":"/on-premises/configuration/kubernetes/index"},"pages":[{"group":"Authentication","icon":"address-card","root":{"title":"Authentication","icon":"address-card","href":"/on-premises/configuration/kubernetes/authentication/index"},"pages":[{"title":"OIDC Authentication","icon":"id-card-clip","href":"/on-premises/configuration/kubernetes/authentication/oidc-authentication"},{"title":"SAML Authentication","icon":"building-columns","href":"/on-premises/configuration/kubernetes/authentication/saml-authentication"},{"title":"LDAP Authentication","icon":"address-book","href":"/on-premises/configuration/kubernetes/authentication/ldap-authentication"},{"title":"Public Access","icon":"lock-open","href":"/on-premises/configuration/kubernetes/authentication/public-access"},{"title":"reCAPTCHA","icon":"robot","href":"/on-premises/configuration/kubernetes/authentication/recaptcha"},{"title":"Password restrictions","icon":"key","href":"/on-premises/configuration/kubernetes/authentication/password-restrictions"}]},{"title":"Sandboxed Compiles","icon":"gear-code","href":"/on-premises/configuration/kubernetes/sandboxed-compiles"},{"title":"Pandoc Import and Export","icon":"file-lines","href":"/on-premises/configuration/kubernetes/pandoc-import-and-export"},{"group":"Integrations","icon":"puzzle-piece","root":{"title":"Integrations","icon":"puzzle-piece","href":"/on-premises/configuration/kubernetes/integrations/index"},"pages":[{"title":"Git integration","icon":"code-branch","href":"/on-premises/configuration/kubernetes/integrations/git-integration"},{"title":"GitHub Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/github.svg","href":"/on-premises/configuration/kubernetes/integrations/github-synchronisation"},{"title":"GitLab Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/gitlab.svg","href":"/on-premises/configuration/kubernetes/integrations/gitlab-synchronisation"},{"title":"Gitea Synchronisation","icon":"mug-hot","href":"/on-premises/configuration/kubernetes/integrations/gitea-synchronisation"},{"title":"Dropbox Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/dropbox.svg","href":"/on-premises/configuration/kubernetes/integrations/dropbox-synchronisation"},{"title":"Zotero Integration","icon":"z","href":"/on-premises/configuration/kubernetes/integrations/zotero-integration"},{"title":"Mendeley Integration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/mendeley.svg","href":"/on-premises/configuration/kubernetes/integrations/mendeley-integration"},{"title":"MCP Server","icon":"plug","href":"/on-premises/configuration/kubernetes/integrations/mcp-server"},{"title":"AI Integration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/openai.svg","href":"/on-premises/configuration/kubernetes/integrations/ai-integration"},{"title":"Overleaf Import API","icon":"rectangle-api","href":"/on-premises/configuration/kubernetes/integrations/overleaf-import-api"}]},{"title":"Templates","icon":"paste","href":"/on-premises/configuration/kubernetes/templates"},{"title":"External URL","icon":"link","href":"/on-premises/configuration/kubernetes/external-url"},{"title":"Logging","icon":"memo-circle-info","href":"/on-premises/configuration/kubernetes/logging"},{"title":"TLS proxy","icon":"lock","href":"/on-premises/configuration/kubernetes/tls-proxy"},{"title":"Branding","icon":"copyright","href":"/on-premises/configuration/kubernetes/branding"},{"title":"Localization","icon":"globe-pointer","href":"/on-premises/configuration/kubernetes/localization"},{"title":"Email delivery","icon":"paper-plane-top","href":"/on-premises/configuration/kubernetes/email-delivery"},{"title":"Redis","icon":"memory","href":"/on-premises/configuration/kubernetes/redis"},{"title":"S3","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/aws.svg","href":"/on-premises/configuration/kubernetes/s3"},{"title":"Adding LaTeX user help","icon":"graduation-cap","href":"/on-premises/configuration/kubernetes/adding-latex-user-help"},{"title":"Horizontal scaling","icon":"layer-group","href":"/on-premises/configuration/kubernetes/horizontal-scaling"}]}]},{"group":"User guide","pages":[{"group":"For administrators","icon":"user-gear","root":{"title":"For administrators","icon":"user-gear","href":"/on-premises/user-guide/administrators/index"},"pages":[{"title":"Onboarding","icon":"user-plus","href":"/on-premises/user-guide/administrators/onboarding"},{"title":"Basic management","icon":"sliders","href":"/on-premises/user-guide/administrators/basic-management"},{"title":"User management","icon":"users-gear","href":"/on-premises/user-guide/administrators/user-management"},{"title":"Project management","icon":"folder-gear","href":"/on-premises/user-guide/administrators/project-management"},{"title":"Template management","icon":"paste","href":"/on-premises/user-guide/administrators/template-management"}]},{"group":"For users","icon":"users","root":{"title":"For users","icon":"users","href":"/on-premises/user-guide/users/index"},"pages":[{"title":"Git integration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/git-alt.svg","href":"/on-premises/user-guide/users/git-integration"},{"title":"GitHub Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/github.svg","href":"/on-premises/user-guide/users/github-synchronisation"},{"title":"GitLab Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/gitlab.svg","href":"/on-premises/user-guide/users/gitlab-synchronisation"},{"title":"Gitea Synchronisation","icon":"mug-hot","href":"/on-premises/user-guide/users/gitea-synchronisation"},{"title":"Dropbox Synchronisation","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/dropbox.svg","href":"/on-premises/user-guide/users/dropbox-synchronisation"},{"title":"Zotero Integration","icon":"z","href":"/on-premises/user-guide/users/zotero-integration"},{"title":"Mendeley Integration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/mendeley.svg","href":"/on-premises/user-guide/users/mendeley-integration"},{"title":"Templates","icon":"paste","href":"/on-premises/user-guide/users/templates"},{"title":"Symbol Palette","icon":"omega","href":"/on-premises/user-guide/users/symbol-palette"},{"title":"Advanced Reference Search","icon":"magnifying-glass","href":"/on-premises/user-guide/users/advanced-reference-search"},{"title":"AI Assistant","icon":"sparkles","href":"/on-premises/user-guide/users/ai-assistant"},{"title":"Error Assistant","icon":"wand-magic-sparkles","href":"/on-premises/user-guide/users/error-assistant"},{"title":"MCP Server","icon":"plug","href":"/on-premises/user-guide/users/mcp-server"},{"title":"Python Runner","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/python.svg","href":"/on-premises/user-guide/users/python-runner"},{"title":"Word import and export","icon":"file-word","href":"/on-premises/user-guide/users/word-import-export"},{"title":"Open in Overleaf","icon":"arrow-up-right-from-square","href":"/on-premises/user-guide/users/open-in-overleaf"},{"title":"Multiple emails","icon":"envelope","href":"/on-premises/user-guide/users/multiple-emails"}]}]},{"group":"Maintenance","pages":[{"title":"docker-compose.yml to Toolkit migration","icon":"right-left","href":"/on-premises/maintenance/docker-compose.yml-to-toolkit-migration"},{"title":"Upgrading your deployment","icon":"arrow-up-from-square","href":"/on-premises/maintenance/upgrading-your-deployment"},{"title":"Upgrading on Kubernetes","icon":"arrow-up-from-square","href":"/on-premises/maintenance/upgrading-on-kubernetes"},{"group":"Data and backups","icon":"database","root":{"title":"Data and backups","icon":"database","href":"/on-premises/maintenance/data-and-backups/index"},"pages":[{"title":"Exporting projects","icon":"file-export","href":"/on-premises/maintenance/data-and-backups/exporting-projects"}]},{"title":"Extending TeX Live","icon":"rectangle-pro","href":"/on-premises/maintenance/extending-tex-live"},{"title":"Updating TeX Live Full Images Automatically","icon":"arrows-rotate","href":"/on-premises/maintenance/updating-tex-live-full-images-automatically"},{"title":"Horizontal scaling","icon":"distribute-spacing-horizontal","href":"/on-premises/maintenance/horizontal-scaling"},{"title":"Small server","icon":"memory","href":"/on-premises/maintenance/small-server"},{"title":"S3 migration","icon":"https://d3gk2c5xim1je2.cloudfront.net/fontawesome/v7.2.0/brands/aws.svg","href":"/on-premises/maintenance/s3-migration"},{"title":"Updating MongoDB","icon":"database","href":"/on-premises/maintenance/updating-mongodb"}]},{"group":"User and project management","pages":[{"title":"Roles and permissions","icon":"list-check","href":"/on-premises/user-and-project-management/roles-and-permissions"},{"group":"User management","icon":"users-between-lines","root":{"title":"User management","icon":"users-between-lines","href":"/on-premises/user-and-project-management/user-management/index"},"pages":[{"title":"Username migration","icon":"lock","href":"/on-premises/user-and-project-management/user-management/username-migration"},{"title":"Migrating to LDAP or SAML","icon":"rectangle-pro","href":"/on-premises/user-and-project-management/user-management/migrating-to-ldap-or-saml"}]},{"group":"Project management","icon":"rectangle-history","root":{"title":"Project management","icon":"rectangle-history","href":"/on-premises/user-and-project-management/project-management/index"},"pages":[{"title":"Bulk transfer of project ownership","icon":"lock","href":"/on-premises/user-and-project-management/project-management/bulk-transfer-of-project-ownership"}]}]},{"group":"Support","pages":[{"title":"Project limits","icon":"list-check","href":"/on-premises/support/project-limits"},{"title":"Troubleshooting","icon":"comments-question-check","href":"/on-premises/support/troubleshooting"},{"title":"Getting help","icon":"truck-medical","href":"/on-premises/support/getting-help"},{"group":"Support guides","icon":"message-question","root":{"title":"Support guides","icon":"message-question","href":"/on-premises/support/support-guides/index"},"pages":[{"title":"Using templates as an individual","icon":"rectangle-vertical-history","href":"/on-premises/support/support-guides/using-templates-as-an-individual"}]}]}]},{"tab":"Blog","icon":"rss","pages":[{"title":"Blog","href":"/blog"}]},{"tab":"TeXLive","icon":"compact-disc","pages":[{"title":"TeXLive","href":"/texlive"}]},{"tab":"Developer","icon":"rectangle-terminal","pages":[{"title":"Developer","href":"/dev"}]}]},{"language":"zh-CN","pages":[{"title":"zh-CN","href":"/zh-CN/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"zh-TW","pages":[{"title":"zh-TW","href":"/zh-TW/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"ja","pages":[{"title":"ja","href":"/ja/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"de","pages":[{"title":"de","href":"/de/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"fr","pages":[{"title":"fr","href":"/fr/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"es","pages":[{"title":"es","href":"/es/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"it","pages":[{"title":"it","href":"/it/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"ko","pages":[{"title":"ko","href":"/ko/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"ru","pages":[{"title":"ru","href":"/ru/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"nl","pages":[{"title":"nl","href":"/nl/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"pt","pages":[{"title":"pt","href":"/pt/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"tr","pages":[{"title":"tr","href":"/tr/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"uk","pages":[{"title":"uk","href":"/uk/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"pl","pages":[{"title":"pl","href":"/pl/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"cs","pages":[{"title":"cs","href":"/cs/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"sv","pages":[{"title":"sv","href":"/sv/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"fi","pages":[{"title":"fi","href":"/fi/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"ar","pages":[{"title":"ar","href":"/ar/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"vi","pages":[{"title":"vi","href":"/vi/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"no","pages":[{"title":"no","href":"/no/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"da","pages":[{"title":"da","href":"/da/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"id","pages":[{"title":"id","href":"/id/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"zh-Hans","pages":[{"title":"zh-Hans","href":"/zh-Hans/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]},{"language":"zh-Hant","pages":[{"title":"zh-Hant","href":"/zh-Hant/on-premises/configuration/overleaf-toolkit/authentication/oidc-authentication"}]}]},"basePath":"","title":"OIDC Authentication - Ayakaleaf Pro","deploymentId":"dpl_DyXGnKeCjZyA3sUdfMJ7FjkdBefg","buildId":"dpl_DyXGnKeCjZyA3sUdfMJ7FjkdBefg","dynamics":["07c022d89b","a74be98ba7"],"chunks":["Frame-D0FT0qQs.js","DynamicMarkdown-CQM9Bhbv.js","zoom-image-lightbox-BQ4tbj_9.js","lightbox-handle-r17bVUz3.js"]}